‘We have to throw technology at the cyber problem,’ Pentagon CIO says五角大楼首席信息官表示:“我们必须用技术来解决网络安全问题。”
DOD must use “the fantastically skilled people that we have in a much more effective way,” Kirsten Davies said.
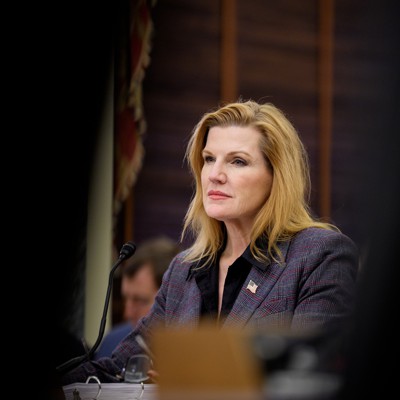
Pentagon Chief Information Officer Kirsten Davies appears at a Senate Committee on Armed Services subcommittee hearing on cybersecurity on Capitol Hill on March 24, 2026 in Washington, DC. Andrew Harnik/Getty Images
DOD must use “the fantastically skilled people that we have in a much more effective way,” Kirsten Davies said.
The Pentagon is shifting its cybersecurity posture to rely more on new capabilities to maintain its digital defenses rather than just bolstering its operational manpower, the department’s IT head said on Wednesday.
Speaking at the Billington Cybersecurity Summit in Washington, D.C., Department of Defense Chief Information Officer Kirsten Davies said, “We can't continue to throw people at the cyber problem; we have to throw technology at the cyber problem.”
Given DOD’s vast size, she said managing cybersecurity means the department has to look at using “everything from automation to machine learning to actually AI,” since the threat environment and range of new and outdated IT systems across its operations presents “a complex Rubik's cube of problems.”
Davies said DOD's thousands of networks include civilian and military components, so “this technology must be ready and available, and it must operate even when it's disconnected.”
Because one small IT problem can ripple across the Pentagon, Davies said it’s also important to “think about leveraging the fantastically skilled people that we have in a much more effective way.”
“As we embrace AI and leverage massive, massive quantities of agentic AI, how do we do that in a way that's supportive of our workforce and provides innovation across that?” she said.
Davies said the department is working to hire employees who know how to use new and emerging tech capabilities, with DOD prioritizing relevant job candidates’ abilities over their educational backgrounds. When it comes to using AI, she said, this means focusing more on applicants who are skilled at prompt engineering — developing instructions for the models to output accurate information.
“Why are we leveraging people for things that technology can do now? Like, let's really build skills and talent that know how to leverage technology very effectively,” Davies said. This mindset has already led to the department working to attract a new crop of cyber professionals.
DOD began accepting applications in July for a new Cyber Registered Apprenticeship Program to bring more cybersecurity talent into the agency, with a particular focus on prioritizing skills-based hiring. The department ultimately closed its first listing four days early after receiving more than 15,000 applications , although DOD has said it plans to open additional rounds of opportunities.
In a previous interview with Nextgov/FCW , Davies said her office was working to transition away from operating as a backend policy shop to taking more of an active role in DOD’s overall mission. She reiterated that mindset on Wednesday, saying that “reform is a big thing for us.”
Davies said this includes reforming the way DOD acquires new products, systems and weaponry. The first step in this process, she noted, was identifying policies and mandates that the department could whittle down or cut entirely — something that equated to more than 60% of relevant DOD guidance.
Now, the department is in the process of carrying out part two of the initiative, which entails looking at the actual process that companies have to go through when it comes to approving new capabilities.
Davies said this process could take anywhere from six to 18 months, but noted that the department just tested out a platform that took that standard timeline “and shortened it to 17 seconds.” She said, however, that the speed of the tested platform is just one component of what the Pentagon must evaluate when it comes to transforming its acquisition strategy.
“That doesn't address what some of the root things are that I still want to address, which is, ‘Are we asking the right questions? Are we demanding the right documentation from software companies?’ Is the output of a 17-second process actually reducing risk?’” she said.
One major step that Davies’ office has taken is its decision to suspend the second-phase requirements for third-party assessments under the Cybersecurity Maturity Model Certification program. The mandatory security framework for defense contractors was stopped in July for a 60-day review by a CMMC Reform Task Force. That assessment period is set to end on Friday.
Davies said the task force has received more than 1,100 responses to a request for information about CMMC’s next steps.
“We wanted to hear more from the defense industrial base on what was important for meaningful, dynamic cybersecurity," she added.
Davies’ remarks came the same day that Washington Technology reported that DOD is moving beyond a suspension of CMMC’s phase two requirements and is effectively implementing a binding regulation that would codify the pause.
NEXT STORY: Top Air and Space Force leaders will gather amid unresolved Iran war, budget uncertainty
2026年3月24日,五角大楼首席信息官克尔斯滕·戴维斯在华盛顿特区国会山出席参议院军事委员会下属小组委员会关于网络安全的听证会。图片来源:Andrew Harnik/Getty Images
克尔斯滕·戴维斯说,国防部必须“以更有效的方式利用我们拥有的技能精湛的人才”。
五角大楼信息技术主管周三表示,五角大楼正在转变其网络安全态势,更多地依靠新技术来维护其数字防御,而不仅仅是加强其作战人员。
美国国防部首席信息官克尔斯滕·戴维斯在华盛顿特区举行的比灵顿网络安全峰会上表示:“我们不能再继续用人力来解决网络安全问题了;我们必须用技术来解决网络安全问题。”
她表示,鉴于国防部的规模庞大,管理网络安全意味着该部门必须考虑使用“从自动化到机器学习再到人工智能的一切技术”,因为其运营中面临的威胁环境以及各种新的和过时的 IT 系统构成了“一个复杂的魔方问题”。
戴维斯表示,国防部的数千个网络包括民用和军事组件,因此“这项技术必须随时可用,即使在断开连接的情况下也必须能够运行”。
戴维斯表示,由于一个小小的 IT 问题可能会波及整个五角大楼,因此“考虑如何更有效地利用我们拥有的技能精湛的人才”也很重要。
她说道:“随着我们拥抱人工智能并利用海量的智能体人工智能,我们如何才能以一种既能支持我们的员工队伍又能促进各领域创新的方式来做到这一点呢?”
戴维斯表示,国防部正努力招聘掌握新兴技术能力的员工,并优先考虑相关求职者的能力而非学历背景。她指出,就人工智能的应用而言,这意味着要更加关注那些擅长快速工程(即编写指令以使模型输出准确信息)的申请人。
“为什么我们要让人力去做一些现在技术就能完成的事情呢?我们应该真正培养能够高效利用技术的技能和人才,”戴维斯说道。这种理念已经促使该部门开始努力吸引一批新的网络安全专业人才。
美国国防部于7月启动了一项新的网络安全注册学徒计划,旨在为该机构招募更多网络安全人才,并特别注重技能型人才的招聘。由于收到了超过15000份申请,国防部最终提前四天关闭了首轮申请,但表示计划开放更多轮次的申请机会。
戴维斯此前在接受Nextgov/FCW采访时表示,她的办公室正在努力转型,从幕后政策部门的角色转变为在国防部的整体任务中发挥更积极的作用。周三,她重申了这一理念,并表示“改革对我们来说至关重要”。
戴维斯表示,这包括改革国防部采购新产品、系统和武器的方式。她指出,这一过程的第一步是确定国防部可以削减或完全取消的政策和指令——这相当于超过60%的相关国防部指导方针。
现在,该部门正在实施该计划的第二部分,即研究公司在批准新功能时必须经历的实际流程。
戴维斯表示,这个过程可能需要6到18个月,但她指出,国防部刚刚测试了一个平台,该平台将标准流程“缩短到了17秒”。不过,她也表示,测试平台的速度只是五角大楼在改革采购战略时必须评估的众多因素之一。
“但这并没有解决我仍然想要解决的一些根本问题,那就是,‘我们问的问题是否正确?我们是否要求软件公司提供正确的文档?’一个 17 秒的流程的输出结果真的能降低风险吗?”她说道。
戴维斯办公室采取的一项重要举措是决定暂停网络安全成熟度模型认证计划(CMMC)第二阶段第三方评估的要求。这项针对国防承包商的强制性安全框架于7月暂停,以便CMMC改革工作组进行为期60天的审查。该审查期将于本周五结束。
戴维斯表示,工作组已收到 1100 多份关于 CMMC 下一步计划的信息请求回复。
她补充说:“我们希望更多地听取国防工业界的意见,了解对于有意义的、动态的网络安全而言,哪些因素是重要的。”
戴维斯发表上述言论的同一天,《华盛顿科技》报道称,美国国防部不再只是暂停 CMMC 第二阶段的要求,而是正在有效地实施一项具有约束力的法规,将暂停措施编入法典。
下一篇报道:在伊朗战争悬而未决、预算不确定性加剧的情况下,空军和太空部队高级领导人将齐聚一堂。