MUIS says human resource management system hit by cybersecurity incident新加坡伊斯兰宗教理事会(MUIS)称,人力资源管理系统遭受网络安全事件攻击
MUIS said the incident does not affect the delivery of public-facing or government services.
MUIS said the incident does not affect the delivery of public-facing or government services.
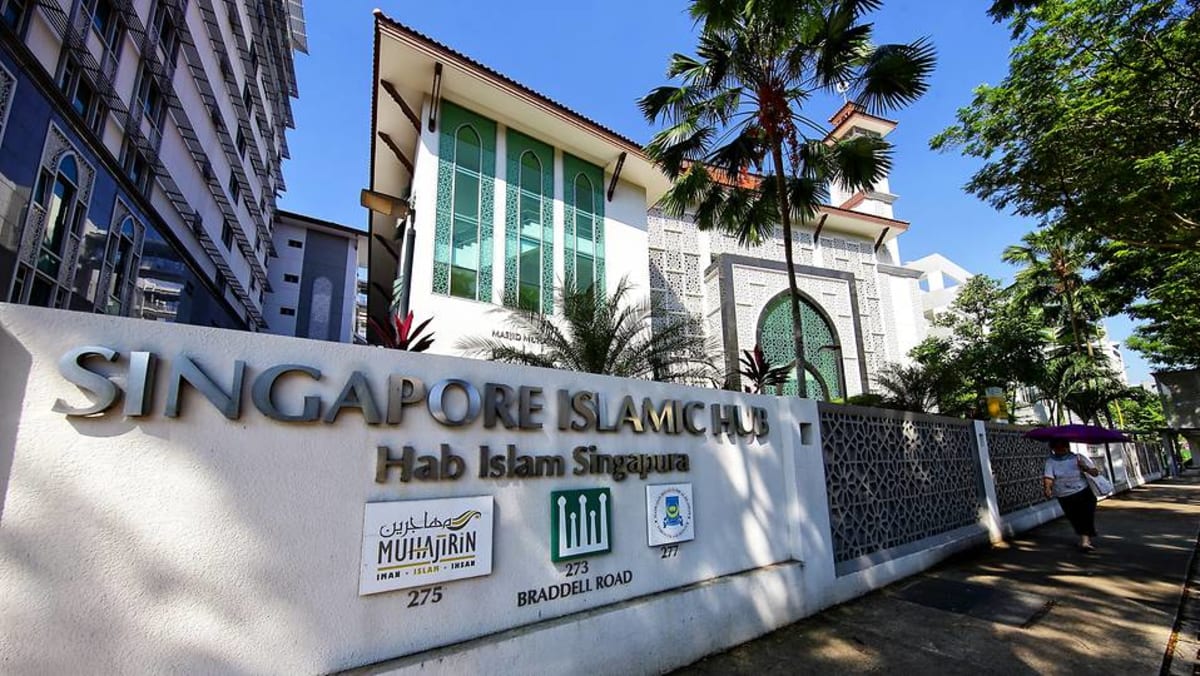
Exterior of the Islamic Religious Council of Singapore (MUIS) building. (Photo: Majlis Ugama Islam Singapura)
This audio is generated by an AI tool.
SINGAPORE: The Islamic Religious Council of Singapore (MUIS) has been hit by a cybersecurity incident involving a human resource management system operated by Singapore-based software vendor Avelogic.
It is working closely with the affected organisations, Avelogic and the relevant authorities on the necessary next steps, said MUIS in response to CNA queries on Tuesday (Sep 15).
The incident does not affect the delivery of public-facing or government services, it added.
“Business continuity arrangements have been implemented to support essential HR and payroll functions, and affected employees are being provided with the necessary guidance and support,” Muis said.
CNA Games Guess Word Crack the word, one row at a time Buzzword Create words using the given letters Mini Sudoku Tiny puzzle, mighty brain teaser Mini Crossword Small grid, big challenge Word Search Spot as many words as you can Show More Show Less MUIS declined to give further information, citing ongoing investigations. It did not specify how many people were affected or what information may have been compromised. The Singapore Police Force confirmed with CNA that a report was lodged and that investigations are ongoing. Separately, Avelogic has published a cybersecurity incident notice on its website concerning its SmartHRMS system. In an update dated Monday, the company said an independent forensic investigation had found no evidence of bulk data exfiltration, based on available Amazon Web Services network telemetry covering confirmed threat actor activity from Aug 30 to Aug 31. Avelogic did not identify the customers affected in the notice. On its website, the company described the SmartHRMS system as "Singapore's CPF-compliant payroll and HR management system for SMEs - automating payroll, leave, claims, employee self-service and attendance in one integrated cloud platform". The company said in the cybersecurity incident notice that core sensitive data fields within SmartHRMS remained protected by application-layer encryption. Avelogic filed a police report on Aug 31 and notified the Personal Data Protection Commission in its capacity as a data intermediary. It commissioned cybersecurity firm Black Panda on Sep 3 to conduct an independent forensic investigation. The firm added that it successfully recovered the last updated data set, and was aiming to get its new system by Friday. “Other components of the system will be brought back online progressively thereafter”, said Avelogic.
MUIS declined to give further information, citing ongoing investigations.
It did not specify how many people were affected or what information may have been compromised.
The Singapore Police Force confirmed with CNA that a report was lodged and that investigations are ongoing.
Separately, Avelogic has published a cybersecurity incident notice on its website concerning its SmartHRMS system.
In an update dated Monday, the company said an independent forensic investigation had found no evidence of bulk data exfiltration, based on available Amazon Web Services network telemetry covering confirmed threat actor activity from Aug 30 to Aug 31.
Avelogic did not identify the customers affected in the notice.
On its website, the company described the SmartHRMS system as "Singapore's CPF-compliant payroll and HR management system for SMEs - automating payroll, leave, claims, employee self-service and attendance in one integrated cloud platform".
The company said in the cybersecurity incident notice that core sensitive data fields within SmartHRMS remained protected by application-layer encryption.
Avelogic filed a police report on Aug 31 and notified the Personal Data Protection Commission in its capacity as a data intermediary.
It commissioned cybersecurity firm Black Panda on Sep 3 to conduct an independent forensic investigation.
The firm added that it successfully recovered the last updated data set, and was aiming to get its new system by Friday.
“Other components of the system will be brought back online progressively thereafter”, said Avelogic.
Get our pick of top stories and thought-provoking articles in your inbox
Stay updated with notifications for breaking news and our best stories
Join our channel for the top reads for the day on your preferred chat app
新加坡伊斯兰宗教理事会(MUIS)表示,该事件不会影响面向公众或政府服务的提供。
新加坡伊斯兰宗教理事会 (MUIS) 大楼的外部。 (照片:新加坡伊斯兰议会)
这段音频由人工智能工具生成。
新加坡:新加坡伊斯兰宗教理事会(MUIS)遭遇网络安全事件,涉及由新加坡软件供应商 Avelogic 运营的人力资源管理系统。
新加坡伊斯兰宗教理事会(MUIS)周二(9月15日)在回复亚洲新闻台(CNA)的询问时表示,他们正在与受影响的组织、Avelogic公司和相关部门密切合作,商讨必要的后续步骤。
声明还补充说,该事件不会影响面向公众或政府服务的提供。
“我们已实施业务连续性安排,以支持必要的人力资源和薪资职能,并向受影响的员工提供必要的指导和支持,”穆伊斯说。
CNA游戏猜词游戏:逐行破解单词;流行词游戏:用给定字母组成单词;迷你数独:小巧的谜题,强大的脑力挑战;迷你填字游戏:小网格,大挑战;单词搜索:尽可能多地找出单词。显示更多 显示更少 新加坡伊斯兰宗教理事会(MUIS)以调查仍在进行为由,拒绝提供更多信息。它没有具体说明有多少人受到影响,也没有说明哪些信息可能已被泄露。新加坡警方已向CNA证实,他们已接到报案,调查正在进行中。此外,Avelogic在其网站上发布了一份关于其SmartHRMS系统的网络安全事件通知。该公司在周一发布的更新中表示,一项独立的取证调查发现,根据8月30日至31日期间已确认的威胁行为者活动的亚马逊网络服务(AWS)网络遥测数据,没有发现大规模数据泄露的证据。Avelogic在通知中没有透露受影响的客户身份。该公司在其网站上将SmartHRMS系统描述为“符合新加坡公积金(CPF)规定的中小企业薪资和人力资源管理系统——在一个集成的云平台上实现薪资、休假、报销、员工自助服务和考勤的自动化管理”。该公司在网络安全事件通知中表示,SmartHRMS中的核心敏感数据字段仍然受到应用层加密的保护。Avelogic于8月31日向警方报案,并以数据中介机构的身份通知了个人数据保护委员会。9月3日,该公司委托网络安全公司Black Panda进行独立的取证调查。该公司补充说,已成功恢复了最后更新的数据集,并计划在周五之前恢复其新系统。“系统的其他组件将随后逐步恢复上线,”Avelogic表示。
新加坡伊斯兰宗教理事会(MUIS)以调查仍在进行为由,拒绝提供更多信息。
声明没有具体说明有多少人受到影响,也没有说明哪些信息可能遭到泄露。
新加坡警方向亚洲新闻台证实,他们已接到报案,目前正在进行调查。
另外,Avelogic 在其网站上发布了一份关于其 SmartHRMS 系统的网络安全事件通知。
该公司在周一发布的一份更新中表示,一项独立的取证调查发现,根据亚马逊网络服务 (AWS) 提供的 8 月 30 日至 8 月 31 日期间已确认的威胁行为者活动网络遥测数据,没有发现大规模数据泄露的证据。
Avelogic公司在通知中并未指明受影响的客户。
该公司在其网站上将 SmartHRMS 系统描述为“符合新加坡 CPF 规定的中小企业薪资和人力资源管理系统——在一个集成的云平台上实现薪资、休假、报销、员工自助服务和考勤的自动化”。
该公司在网络安全事件通知中表示,SmartHRMS 中的核心敏感数据字段仍然受到应用层加密的保护。
Avelogic 于 8 月 31 日向警方报案,并以数据中介机构的身份通知了个人数据保护委员会。
9月3日,该公司委托网络安全公司黑熊猫进行独立取证调查。
该公司补充说,已成功恢复了最新更新的数据集,并计划在周五之前启用新系统。
Avelogic公司表示:“此后,系统的其他组件将逐步恢复上线。”
订阅我们的邮件,即可获取精选热点新闻和引人深思的文章。
订阅通知,第一时间获取突发新闻和精彩报道。
加入我们的频道,即可在您常用的聊天应用上获取当日热门文章。