Nearly 100,000 Bee Cheng Hiang customers' email addresses exposed in first AI-related data breach in Singapore新加坡首例人工智能相关数据泄露事件:美珍香餐厅近10万名顾客的电子邮件地址曝光
"The incident was caused by a human error in developing the email distribution code with an AI tool," said the Personal Data Protection Commission.
"The incident was caused by a human error in developing the email distribution code with an AI tool," said the Personal Data Protection Commission.
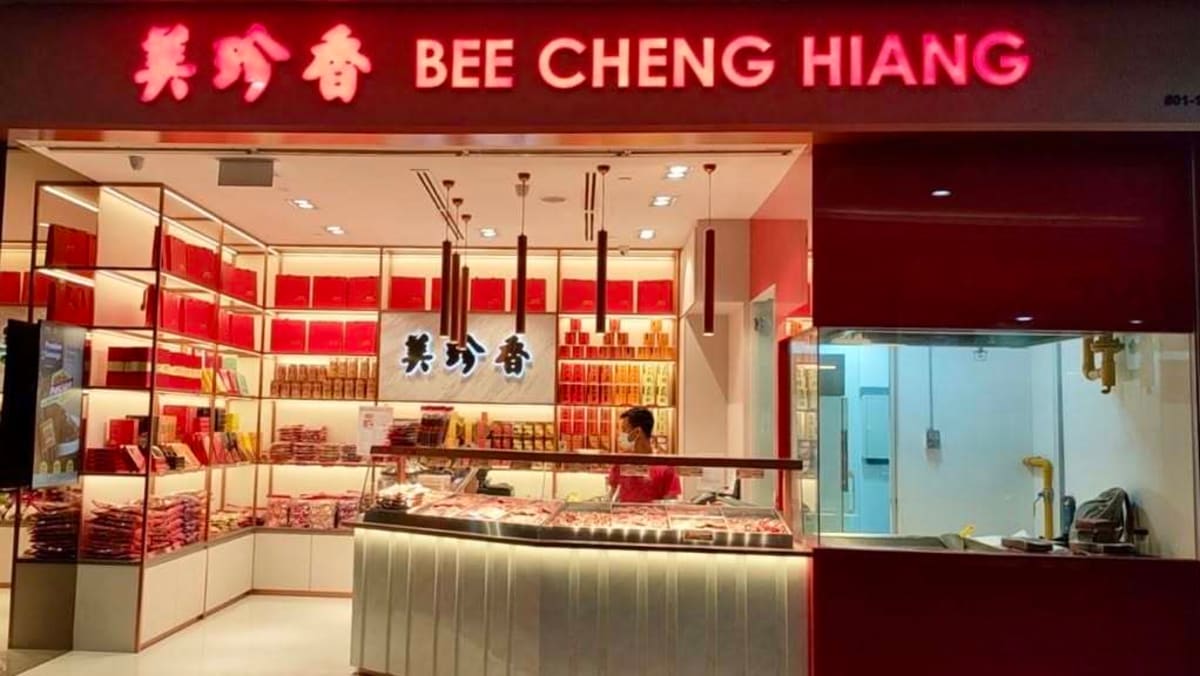
A Bee Cheng Hiang shop near Lavender MRT station. (Photo: Facebook/Bee Cheng Hiang Singapore)
This audio is generated by an AI tool.
SINGAPORE: The email addresses of nearly 100,000 Bee Cheng Hiang customers were disclosed without consent in what the Personal Data Protection Commission said on Wednesday (Sep 30) was the first AI-related data breach in Singapore that it has been notified of.
The breach occurred in April after a Bee Cheng Hiang employee used an AI tool to generate a Python script to distribute a marketing email. The resulting code caused the recipients' email addresses to be visible to everyone, affecting a total of 95,364 customers .
"The incident was caused by a human error in developing the email distribution code with an AI tool," the PDPC said in response to queries from CNA.
According to a statement posted on its website on Sep 21, PDPC said the incident was "not a malfunction in the AI tool", but a result of the prompt given to it by the employee.
CNA Games Guess Word Crack the word, one row at a time Buzzword Create words using the given letters Mini Sudoku Tiny puzzle, mighty brain teaser Mini Crossword Small grid, big challenge Word Search Spot as many words as you can Show More Show Less PDPC said the employee had prompted the AI tool to write a programme to send a "mass email using a local list" in batches, without specifically telling it to hide the email addresses of the other recipients. "The employee did not realise the error before deploying the script, as testing was done by checking activity logs without reviewing the contents of the actual test email," said PDPC. It added that the affected data "was not managed, processed, or generated by any AI-powered operation or process", and that there was "no evidence of further misuse" of the data. The PDPC noted that Bee Cheng Hiang took prompt remedial actions, including immediately stopping the bulk marketing email distribution process, correcting the erroneous script and informing affected customers. The company also introduced a requirement for at least two staff members to verify all bulk email communications. The PDPC noted that this is Bee Cheng Hiang's first attempt at incorporating AI tools into its business operations. "Prior to adopting AI tools to enhance the efficiency of their business operations, organisations should carry out appropriate data protection impact assessments; develop policies and processes; and implement testing and review mechanisms, to ensure that their employees use AI tools responsibly and safeguard personal data." Taking into account the circumstances of the case, t he PDPC accepted a voluntary undertaking from Bee Cheng Hiang to improve its compliance with the Personal Data Protection Act.
PDPC said the employee had prompted the AI tool to write a programme to send a "mass email using a local list" in batches, without specifically telling it to hide the email addresses of the other recipients.
"The employee did not realise the error before deploying the script, as testing was done by checking activity logs without reviewing the contents of the actual test email," said PDPC.
It added that the affected data "was not managed, processed, or generated by any AI-powered operation or process", and that there was "no evidence of further misuse" of the data.
The PDPC noted that Bee Cheng Hiang took prompt remedial actions, including immediately stopping the bulk marketing email distribution process, correcting the erroneous script and informing affected customers.
The company also introduced a requirement for at least two staff members to verify all bulk email communications.
The PDPC noted that this is Bee Cheng Hiang's first attempt at incorporating AI tools into its business operations.
"Prior to adopting AI tools to enhance the efficiency of their business operations, organisations should carry out appropriate data protection impact assessments; develop policies and processes; and implement testing and review mechanisms, to ensure that their employees use AI tools responsibly and safeguard personal data."
Taking into account the circumstances of the case, t he PDPC accepted a voluntary undertaking from Bee Cheng Hiang to improve its compliance with the Personal Data Protection Act.
Get our pick of top stories and thought-provoking articles in your inbox
Stay updated with notifications for breaking news and our best stories
Join our channel for the top reads for the day on your preferred chat app
个人数据保护委员会表示:“该事件是由于在使用人工智能工具开发电子邮件分发代码时出现人为错误造成的。”
位于薰衣草地铁站附近的碧珍香店铺。(图片:Facebook/Bee Cheng Hiang Singapore)
这段音频由人工智能工具生成。
新加坡:新加坡个人数据保护委员会周三(9月30日)表示,美珍香近10万名顾客的电子邮件地址未经同意被泄露,这是新加坡首例与人工智能相关的数据泄露事件。
此次数据泄露事件发生在四月份,当时美珍香的一名员工使用人工智能工具生成了一段Python脚本来发送营销邮件。生成的代码导致收件人的电子邮件地址对所有人可见,共计95,364名客户受到影响。
菲律宾个人数据保护委员会(PDPC)在回复亚洲新闻台(CNA)的询问时表示:“该事件是由于在使用人工智能工具开发电子邮件分发代码时出现人为错误造成的。”
根据菲律宾国家数据保护委员会 (PDPC) 9 月 21 日在其网站上发布的声明,该事件“并非人工智能工具出现故障”,而是由于员工向其发出的指令所致。
CNA游戏猜词游戏:逐行破解单词;流行词游戏:用给定字母造词;迷你数独:小巧的谜题,强大的脑力挑战;迷你填字游戏:小网格,大挑战;单词搜索:尽可能多地找出单词。显示更多 显示更少 个人数据保护委员会(PDPC)表示,该员工指示人工智能工具编写程序,使用本地列表分批发送“群发邮件”,但并未明确指示其隐藏其他收件人的电子邮件地址。PDPC表示:“该员工在部署脚本前并未意识到错误,因为测试是通过查看活动日志进行的,而没有审查实际测试邮件的内容。” PDPC补充说,受影响的数据“并非由任何人工智能驱动的操作或流程管理、处理或生成”,并且“没有证据表明数据被进一步滥用”。PDPC指出,碧清香已迅速采取补救措施,包括立即停止批量营销邮件的发送流程、更正错误脚本并通知受影响的客户。该公司还规定,至少需要两名员工来验证所有批量电子邮件通信。个人数据保护委员会(PDPC)指出,这是美珍香首次尝试将人工智能工具融入其业务运营。“在采用人工智能工具提升业务运营效率之前,机构应进行适当的数据保护影响评估;制定相关政策和流程;并实施测试和审查机制,以确保员工负责任地使用人工智能工具并保护个人数据。” 考虑到本案的具体情况,PDPC接受了美珍香的自愿承诺,即改善其对《个人数据保护法》的遵守情况。
PDPC表示,该员工指示人工智能工具编写程序,使用本地列表分批发送“群发邮件”,但没有明确指示该工具隐藏其他收件人的电子邮件地址。
PDPC表示:“该员工在部署脚本之前没有意识到错误,因为测试是通过检查活动日志进行的,而没有查看实际测试电子邮件的内容。”
声明还补充说,受影响的数据“并非由任何人工智能驱动的操作或流程管理、处理或生成”,并且“没有证据表明数据遭到进一步滥用”。
PDPC注意到,碧成香迅速采取了补救措施,包括立即停止批量营销电子邮件分发流程、纠正错误脚本并通知受影响的客户。
该公司还规定,所有批量电子邮件通信至少需要两名员工进行核实。
菲律宾药品定价委员会指出,这是美珍香首次尝试将人工智能工具融入其业务运营中。
“在采用人工智能工具来提高业务运营效率之前,各组织应进行适当的数据保护影响评估;制定政策和流程;并实施测试和审查机制,以确保员工负责任地使用人工智能工具并保护个人数据。”
考虑到案件的具体情况,个人数据保护委员会接受了 Bee Cheng Hiang 的自愿承诺,以改善其对《个人数据保护法》的遵守情况。
订阅我们的邮件,即可获取精选热点新闻和引人深思的文章。
订阅通知,第一时间获取突发新闻和精彩报道。
加入我们的频道,即可在您常用的聊天应用上获取当日热门文章。