New cyber incident helpline promises triage callback within two hours新推出的网络安全事件求助热线承诺两小时内回电。
Businesses can seek advice from the helpline on phishing, business e-mail compromise, malware and ransomware attacks. Read more at straitstimes.com.
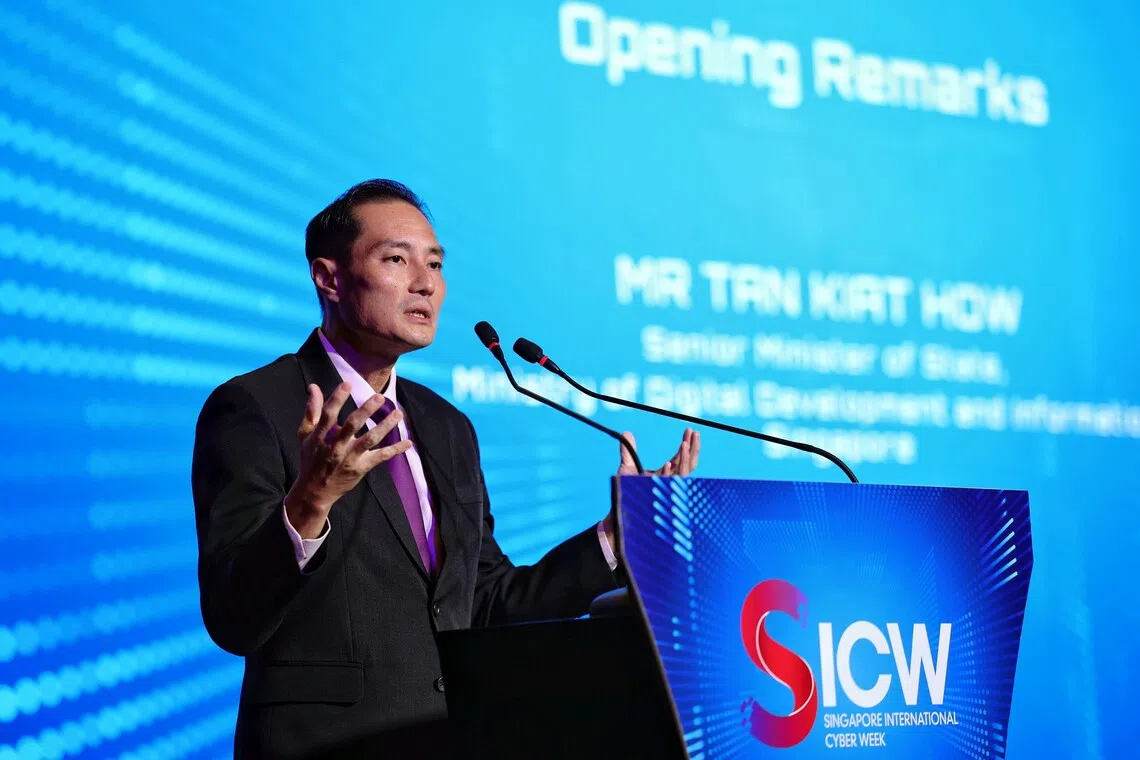
Senior Minister of State for Digital Development and Information Tan Kiat How giving a speech at the Singapore International Cyber Week 2026 in Marina Bay Sands Expo and Convention Centre on Oct 13.
Published Oct 14, 2026, 03:30 PM
Updated Oct 14, 2026, 03:30 PM
SINGAPORE – Organisations hit by cyber incidents can get a triage callback within two hours through a new helpline run by the Singapore Business Federation (SBF).
The free service aims to offer advice on containing cyber incidents and refer callers to specialists for further help, amid increasing cyberattacks and scams.
“For a small business, the first few hours after something goes wrong can be particularly difficult... Taking the right steps early can help contain an incident and manage its impact, but small and medium enterprises may not know where to start and who to turn to,” said Senior Minister of State for Digital Development and Information Tan Kiat How, in launching the Cyber Incident Helpline at Singapore International Cyber Week on Oct 14.
“The goal is simple: To help businesses move quickly from uncertainty to action, respond effectively and recover with as little disruption as possible. Because when an incident happens, time matters,” he added.
Released on Oct 14, the second Singapore Cybersecurity Health Report found that almost nine in 10 organisations surveyed had encountered at least one cybersecurity incident in 2025, up from eight in 10 in the first edition of the report in 2023.
The most commonly reported incidents are ransomware, compromised credentials and social engineering, according to the survey of more than 2,000 businesses and non-profit organisations in Singapore between October and November 2025.
Tan said that the helpline aims to provide guidance for small and medium-sized enterprises without dedicated cybersecurity staff or established incident response arrangements.
The survey report, released by the Cyber Security Agency of Singapore (CSA), showed a mixed picture of organisations’ ability to manage cyberthreats.
Compared with the first edition conducted in 2023, fewer organisations reported business impacts from cyber incidents. For example, the proportions of businesses reporting incident response costs, business disruption and financial losses declined by 3.8, 3.1 and 2.7 percentage points respectively.
However, progress in strengthening their defences was uneven.
Adoption of measures to keep software and systems updated rose from 72 per cent to 80 per cent, while adoption of measures to prepare for and respond to incidents fell from 76 per cent to 73 per cent.
A lack of expertise and resources continued to hinder efforts to strengthen defences.
Among businesses polled, 56 per cent cited insufficient cybersecurity knowledge and experience as a barrier, while 37 per cent cited insufficient manpower and resources.
For businesses unsure what to do when a cyber incident occurs, the new helpline offers initial guidance. They can submit details of the incident at cyberresilience.sg or call 6890-9555 from 8am to 6pm on weekdays, excluding public holidays.
A trained operator will assess the nature and urgency of the issue before a representative calls back to gather further information and recommend immediate steps to limit the incident’s spread and impact.
Businesses can seek advice on threats including phishing, business e-mail compromise, malware and ransomware, unauthorised access and suspected data breaches. If specialist intervention is needed, they may receive a list of pre-approved cybersecurity providers they can engage for remediation and recovery.
The helpline’s role is advisory: It does not investigate attacks, collect digital evidence, troubleshoot systems remotely or restore systems and data. Businesses remain responsible for choosing their service providers and reporting incidents to regulators or the authorities.
SBF vice-chairman and honorary treasurer Chin Wei Jia said that the helpline is being supported by a dedicated cybersecurity team in the initial phase of its launch, and the foundation will monitor industry demand, utilisation patterns and operational requirements before any potential enhancements.
The service expands the work of the Cyber Resilience Centre, which SBF established in 2025 to help organisations prepare for cyberthreats through health clinics, workshops and exercises.
The challenges facing SMEs were also highlighted in CSA’s latest Singapore Cyber Landscape report released on June 30. It recorded 165 reported ransomware cases in 2025, up from 159 in 2024, with SMEs disproportionately affected because of their comparatively weaker cybersecurity capabilities and limited resources.
While that report examines broader cyberthreats and their implications for Singapore, the health survey focuses on local organisations’ experiences and defences.
SME/Small and medium-sized enterprise
新加坡数码发展及新闻部高级政务部长陈杰豪于10月13日在滨海湾金沙会展中心举行的2026年新加坡国际网络周上发表讲话。
发布于2026年10月14日下午3:30
更新于2026年10月14日下午3:30
新加坡——遭受网络攻击的机构可以通过新加坡商业联合会(SBF)开通的新热线,在两小时内获得初步评估回电。
这项免费服务旨在为控制网络安全事件提供建议,并将致电者转介给专家以获得进一步帮助,以应对日益增多的网络攻击和诈骗。
“对于小企业来说,发生意外后的最初几个小时可能尤其艰难……及早采取正确的措施有助于控制事件并控制其影响,但中小企业可能不知道从哪里开始以及应该向谁求助,”新加坡数字发展及新闻部高级政务部长陈杰豪在10月14日新加坡国际网络安全周上启动网络安全事件求助热线时表示。
“目标很简单:帮助企业迅速从不确定状态过渡到行动状态,有效应对并尽可能减少中断地恢复运营。因为当突发事件发生时,时间至关重要。”他补充道。
10 月 14 日发布的第二份新加坡网络安全健康报告发现,在 2025 年,近 90% 的受访机构至少遭遇过一次网络安全事件,高于 2023 年第一版报告中的 80%。
根据 2025 年 10 月至 11 月期间对新加坡 2000 多家企业和非营利组织的调查,最常报告的事件是勒索软件、凭证泄露和社会工程攻击。
Tan表示,该热线旨在为没有专门的网络安全人员或已建立的事件响应机制的中小型企业提供指导。
新加坡网络安全局 (CSA) 发布的调查报告显示,各组织应对网络威胁的能力参差不齐。
与2023年首次开展的调查相比,报告网络安全事件对业务造成影响的机构数量有所减少。例如,报告事件响应成本、业务中断和财务损失的企业比例分别下降了3.8、3.1和2.7个百分点。
然而,他们在加强防御方面的进展并不均衡。
为保持软件和系统更新而采取的措施的比例从 72% 上升到 80%,而为应对突发事件而采取的措施的比例从 76% 下降到 73%。
专业知识和资源的匮乏继续阻碍着加强防御的努力。
在接受调查的企业中,56% 的企业表示网络安全知识和经验不足是一个障碍,而 37% 的企业表示人力和资源不足。
对于不确定如何应对网络安全事件的企业,新的热线可提供初步指导。他们可以在 cyberresilience.sg 网站上提交事件详情,或在工作日(公共假期除外)上午 8 点至下午 6 点拨打 6890-9555。
经过培训的接线员将评估问题的性质和紧迫性,然后由代表回电收集更多信息,并建议立即采取措施来限制事件的蔓延和影响。
企业可以就网络钓鱼、商业电子邮件入侵、恶意软件和勒索软件、未经授权的访问以及疑似数据泄露等威胁寻求建议。如果需要专家介入,他们可能会收到一份预先批准的网络安全服务提供商名单,以便聘请他们进行补救和恢复工作。
该热线仅提供咨询服务:它不负责调查攻击事件、收集数字证据、远程排除系统故障或恢复系统和数据。企业仍需自行负责选择服务提供商,并向监管机构或有关部门报告安全事件。
新加坡银行基金会副主席兼名誉司库秦伟嘉表示,该热线在推出初期由专门的网络安全团队提供支持,基金会将在进行任何潜在改进之前,监测行业需求、使用模式和运营要求。
该服务扩展了网络弹性中心的工作范围,该中心由 SBF 于 2025 年成立,旨在通过健康诊所、研讨会和演习帮助组织做好应对网络威胁的准备。
新加坡网络安全局 (CSA) 于 6 月 30 日发布的最新《新加坡网络安全形势报告》也重点强调了中小企业面临的挑战。报告显示,2025 年报告的勒索软件案件数量为 165 起,高于 2024 年的 159 起,中小企业由于网络安全能力相对较弱且资源有限,受到的影响尤为严重。
虽然该报告探讨了更广泛的网络威胁及其对新加坡的影响,但健康调查则侧重于本地组织的经验和防御措施。
中小企业