Firms in Singapore should ‘act now’ to fix critical PHP vulnerabilities:新加坡企业应“立即采取行动”修复关键的PHP漏洞:
PHP vulnerabilities had resided in the software for years until they were uncovered by AI. Read more at straitstimes.com.
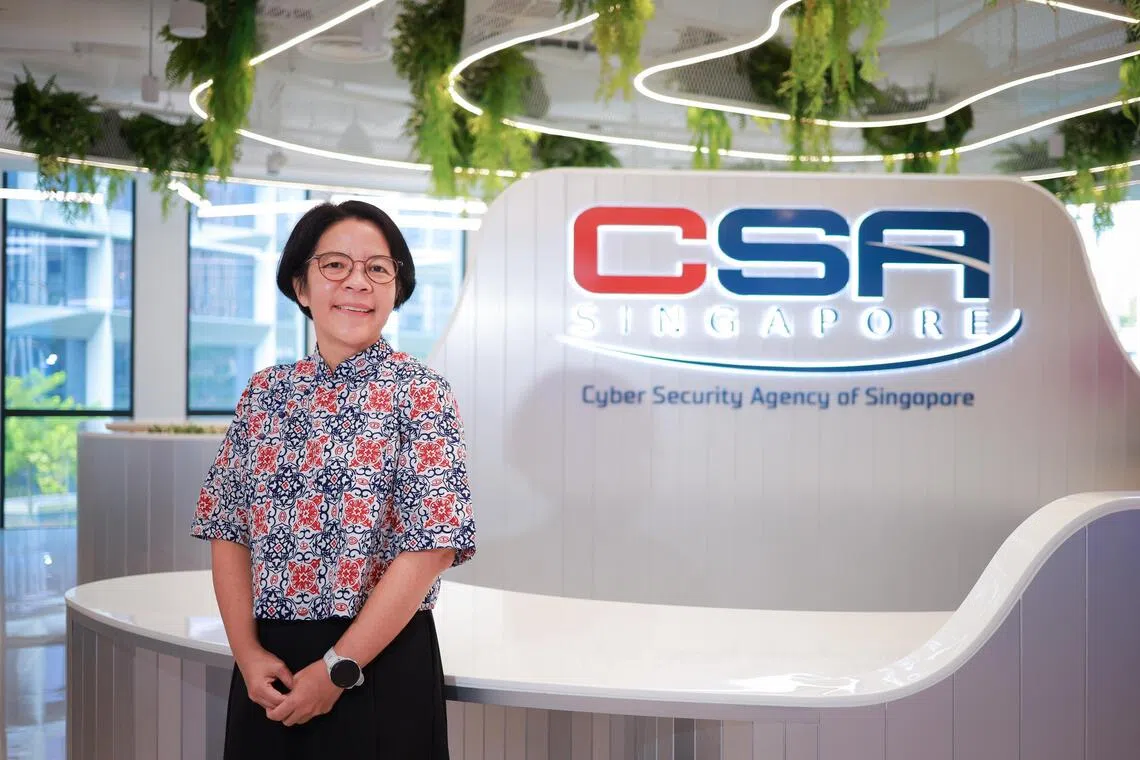
On Oct 22, Singapore’s Commissioner of Cybersecurity Gwenda Fong urged firms to address critical vulnerabilities in PHP, a programming language that powers a large share of the internet.
Published Oct 22, 2026, 07:52 PM
Updated Oct 22, 2026, 07:52 PM
SINGAPORE - Organisations in Singapore should act now to address critical vulnerabilities in PHP, a programming language that powers a large share of the internet, said Singapore’s Commissioner of Cybersecurity Gwenda Fong on Oct 22.
Her comment on LinkedIn comes after cybersecurity agencies across the world warned about two critical vulnerabilities discovered in PHP on Oct 21.
PHP developers released fixes on Oct 21 for vulnerabilities that had resided in the software for years until they were uncovered by artificial intelligence tools.
These warnings prompted governments and companies worldwide to shut down websites and apps as they raced to protect themselves from potential cyber attacks.
“My message to every organisation in Singapore is simple: do not wait,” said Fong, who is also chief executive of the Cyber Security Agency of Singapore (CSA).
She said that many organisations, especially small and medium-sized enterprises that rely on external IT vendors or hosting providers, may not realise that their systems are affected. But she said that the threat is immediate.
“CSA is working urgently with government agencies, Critical Information Infrastructure owners, major enterprises and industry partners to accelerate patching. We are also reaching out through business associations, cybersecurity service providers and technology partners to help smaller organisations take action,” she said.
Fong said that those who operate websites or online services should check whether their systems, including those managed by third-party vendors, use affected versions of PHP.
They should also patch immediately, prioritising internet-facing systems, and investigate whether there are signs that their systems may already have been compromised.
“If you are unsure whether your organisation is affected, contact your IT team, website developer or hosting provider today,” she said.
“Cybersecurity is a shared responsibility. Acting quickly now can prevent a vulnerability from becoming a serious incident.”
She referred those who require technical guidance and updates to CSA’s SingCERT alert .
On Oct 21, CSA said that the exposed vulnerabilities affect all versions of the scripting language. Even though there are no known cases of websites here taken down by hackers, CSA said: “There have been reports of widespread exploitation attempts targeting these vulnerabilities, as well as the development of multiple proof-of-concept exploits.”
GovTech, which powers Singapore’s digital government, said it is working closely with government agencies to implement the necessary precautionary measures.
“There is currently no indication that any Government systems have been compromised as a result of these vulnerabilities,” said GovTech.
“Where necessary, affected services may be temporarily taken offline to facilitate remediation. Such measures are precautionary and do not indicate that the systems have been compromised.”
A Reuters report quoted Madeline Lawrence, co-founder of Belgian cybersecurity firm Aikido Security, as saying: “Details of these flaws became public before fixes were ready, and attacks have since been reported.”
AI/artificial intelligence
10 月 22 日,新加坡网络安全专员方格文敦促各公司解决 PHP 编程语言中的关键漏洞,PHP 是互联网很大一部分的底层编程语言。
发布于 2026 年 10 月 22 日晚上 7:52
更新于2026年10月22日晚上7:52
新加坡——新加坡网络安全专员方格文达 (Gwenda Fong) 于 10 月 22 日表示,新加坡的各组织机构应立即采取行动,解决 PHP(一种为互联网很大一部分提供支持的编程语言)中的关键漏洞。
在她发表LinkedIn评论之前,世界各地的网络安全机构于10月21日警告称,PHP中发现了两个严重漏洞。
PHP 开发人员于 10 月 21 日发布了修复程序,以修复软件中存在多年的漏洞,这些漏洞直到被人工智能工具发现才被发现。
这些警告促使世界各国政府和公司纷纷关闭网站和应用程序,以保护自己免受潜在的网络攻击。
“我对新加坡所有机构的信息很简单:不要等待,”方先生说道,他同时也是新加坡网络安全局(CSA)的首席执行官。
她表示,许多机构,尤其是依赖外部IT供应商或托管服务提供商的中小型企业,可能并未意识到其系统已受到影响。但她强调,威胁迫在眉睫。
“CSA正与政府机构、关键信息基础设施所有者、大型企业和行业合作伙伴紧急合作,加快漏洞修补工作。我们还通过商业协会、网络安全服务提供商和技术合作伙伴,帮助小型组织采取行动,”她说道。
方表示,运营网站或在线服务的用户应该检查他们的系统(包括第三方供应商管理的系统)是否使用了受影响的 PHP 版本。
他们还应立即进行修补,优先修补面向互联网的系统,并调查是否有迹象表明他们的系统可能已被入侵。
“如果您不确定您的组织是否受到影响,请立即联系您的 IT 团队、网站开发人员或托管服务提供商,”她说。
“网络安全是每个人的责任。现在迅速采取行动可以防止漏洞演变成严重事件。”
她建议那些需要技术指导和更新的人参考 CSA 的 SingCERT 警报。
10月21日,加拿大安全局(CSA)表示,此次暴露的漏洞影响所有版本的脚本语言。尽管目前尚未有网站因黑客攻击而瘫痪的案例,但CSA指出:“已有报告显示,针对这些漏洞的大规模利用尝试,以及多个概念验证漏洞的开发。”
新加坡政府科技局(GovTech)是新加坡数字政府的技术支持机构,该机构表示正与政府机构密切合作,落实必要的预防措施。
GovTech表示:“目前没有任何迹象表明,由于这些漏洞,任何政府系统都受到了损害。”
“如有必要,受影响的服务可能会暂时离线以进行修复。此类措施属于预防措施,并不表示系统已被入侵。”
路透社的一篇报道援引比利时网络安全公司 Aikido Security 联合创始人 Madeline Lawrence 的话说:“这些漏洞的细节在修复程序完成之前就已经公开了,此后也出现了攻击事件。”
人工智能