The Truth About Cyber Warfare’s Impact On Airpower网络战对空中力量影响的真相
There's a lot of bad info out there about how the cyber and aerial domains of warfare will converge. Here's the reality, for better or worse.
Updated Aug 18, 2021 6:03 PM EDT
It has become relatively commonplace in policy and military circles for the term ‘cyber’ to be attached to lists of both threats to and enablers for traditional airpower capabilities. Cyberweapons are without doubt an important tool in warfare, espionage, and deterrence. The potential attack surface against which they can be employed is increasing rapidly as ever more of the fabric of society becomes digitized and network-enabled. However, the tempo and nature of the processes by which military-grade cyber capabilities can be developed and deployed are regularly misunderstood in non-specialist circles. Confusion over where the boundaries lie between offensive electronic warfare and cyber capabilities can further distort public discussions of how these important capabilities fit into conventional military operations, and the application of airpower, in particular.
Broadly, the fundamental dividing line between electronic warfare (EW) and cyber is that where offensive EW capabilities are designed to interact with hostile systems using electromagnetic energy emissions, offensive cyber capabilities are designed to interact with hostile systems using data in the form of code. In practice, the boundaries between the two spheres of operations are often somewhat blurred. This is especially true as an increasing number of platforms such as the US Navy’s EA-18G Growler and the F-35 Lightning II are fielded with systems and sensors which can potentially interact with enemy systems using both EW and cyber techniques, and in some cases transition quickly from one to the other in flight.
There are also similarities in that designing effective military EW and cyber capabilities require a detailed understanding of the target systems or networks, which must be refreshed frequently in order to remain relevant. However, the timescales involved in developing electronic attack capabilities and offensive cyber capabilities against military systems are very different. This is because of how cyberattacks work.
The EA-18G is an electronic warfare platform, but its mission may also bleed into the cyber domain., U.S. Navy photo by Cmdr. Ian C. Anderson, USN
A military cyberattack functions, in essence, by the accessing, alteration, or deletion of data held within a hostile network. This is done in the virtual domain so as to achieve an effect in the real world. As such, a cyberattack can serve a wide range of purposes depending on what data is being accessed and what its intended function is within its host network and/or system. Effects of a successful attack range from gaining detailed intelligence on how threat systems work, preventing a target system from performing its function correctly, temporarily disabling key functions, or even causing it to malfunction in such a way as to cause physical damage.
This article is sponsored by Private Internet Access
However, before any desired effects can be designed into a cyber payload, an attacker must work out what data is held in which adversary networks, and what coding language and programming logic is being used in those networks. Many civilian networks use commercially available and, therefore, easily understood coding languages and logic. This makes penetrating and subsequently exploiting such systems significantly easier than sensitive military systems which are purpose-built and regularly monitored. In either case, a cyber attacker must gain an initial access point to discover and then extract data to reveal what is stored on a given network and how it is coded.
The U.S. military is in a race to create cyber weapons and defend against them., USAF
This vital first step in planning any cyberattack must be done without the data breach being identified as a hostile presence. In the case of bespoke military systems, this task is made more difficult by the fact that the attackers will not be initially familiar with the coding language and rules of the network, and thus will struggle to mimic legitimate network traffic well enough to avoid rapid detection.
If an attacker is detected, then they will not only be rapidly isolated from the network, but may also be counter-attacked using the gateway connection they have created. The most sensitive military systems are also generally air-gapped, which means that they have no interfaces, either wired or wireless, to outside networks or the wider internet. As such, in order to conduct initial network reconnaissance, attackers will need to bypass physical isolation measures and then set up a remote access connection for data exfiltration and future penetration attempts.
Once a network has been identified as containing useful target data for theft, modification, or deletion, an attacker must attempt to bypass security measures and gain control over administrator accounts which will then grant the necessary permissions. Since almost all military and sensitive civilian systems are protected by multifactor authentication security measures, this either requires human intelligence assets to willingly or unwillingly give up passwords, keys, and biometrics, or hacking to bypass those security measures.
A cyber warfare operations officer watches members of the 175th Cyberspace Operations Group analyze log files and provide a cyber threat update utilizing a Kibana visualization on the large data wall in the Hunter’s Den at Warfield Air National Guard Base, Middle River, Maryland. , J.M. Eddins Jr./U.S. Air Force
Hacking involves finding ambiguities or errors in the coding of a network that can be exploited to bypass the need to enter authentication information. Most complex systems have potential vulnerabilities, but sensitive networks will also be checked and patched regularly to remove any that are discovered by chance or exposed by a detected attack attempt.
Once access to the required administrator nodes is gained by an attacker, they can leverage them to alter and insert data, including cyber weapons. A cyber weapon is a package of code, typically carefully calibrated to perform a specific function within a specific networked system while making attribution and detection as difficult as possible for defenders. Once inserted successfully, a cyber payload may be triggered immediately. However, if it is intended to be used in the future it must be coded to either trigger automatically when certain conditions are met, otherwise, access must be re-established to trigger it at a desired point in time.
Many military systems operate under emission control posture for extended periods when operating against modern opposing forces, and in the case of ships, mobile surface-to-air missile (SAM) systems, and aircraft in flight, they are also physically isolated from most potential access methods. Software is also regularly updated and patched, which can result in the vulnerability being used for access being deliberately or inadvertently shut off before a cyber weapon’s payload can be triggered.
S-400 air defense system control element., Russian MoD
Software updates can also change the internal logic of a system such that a previously emplaced cyber capability no longer functions as intended when triggered. Furthermore, military networks tend to be protected by real-time monitoring of all traffic across the limited number of known access points. Therefore, each access attempt to either trigger, assure or update an emplaced cyber weapon capability risks detection and subsequent purging or counterattack by the network defenders.
The practical upshot is that developing a cyber capability against a sensitive hostile military asset such as air defense early warning networks, aircraft avionics, or intelligence processing systems takes years of concentrated effort and carries significant risks of discovery and attribution. Furthermore, once established, there is no guarantee that the capability can be triggered on-demand in support of a future kinetic operation, nor that it will not be discovered or patched into irrelevance by enemy cyber defenses before it can be used.
There is also no way to predict with certainty the various potential second and third-order effects if the payload escapes beyond the confines of the system it was designed to attack. Therefore, such capabilities are viewed in most nations as strategic level military tools, and knowledge of their existence, capabilities, and limitations is held at a very high level of classification. Release authorization is also typically held at a much more senior level of the military and political command structure than conventional military assets.
The length of time required to establish capabilities in sensitive, hostile networks, and the difficulties of assurance and triggering for emplaced payloads significantly affect how cyber capabilities interact with the air domain. One of the most important uses of cyber capabilities over the medium to long term is to gather sensitive information about critical enemy systems such as radars, missile guidance logic, or seeker performance. Such data is critical for programming effective aircraft countermeasure systems, electronic warfare suites, optimizing tactics for terminal missile evasion, and far more.
An F-35 prototype undergoes electromagnetic testing in an anechoic chamber. , Lockheed Martin-Jack Noble
Publicly acknowledged cyber breaches aimed at obtaining this sort of information on American air systems suggest that most state attacks target the industrial supply chain rather than bespoke military systems. This would make sense since the supply chain in many modern aerial combat and air weapons programs is multinational and diverse, which makes finding vulnerabilities and networks with lax security measures easier for attackers. It also has implications for the potential areas of vulnerability for combat air capabilities to more direct cyberattacks in a future conflict.
The closed and heavily monitored nature of most avionics and mission systems make direct cyberattacks on aircraft and command systems difficult (although perhaps not impossible) for adversaries to accomplish in practice. However, it would not be surprising if less heavily defended ancillary logistics and industrial supply networks suddenly started to malfunction or fail during critical phases of a future state-on-state conflict as a result of previously embedded hostile cyber payloads.
If spare parts are not delivered reliably, then even the simplest combat aircraft will rapidly lose effectiveness, as fleets are cannibalized to maintain a steadily decreasing number of jets ready to fly and fight. If munitions and fuel cannot be supplied, then effectiveness and sortie rates will drop even more rapidly. As the extent of digitization of the supply and maintenance chain on which western air forces depend becomes ever greater, the potential attack surface also expands.
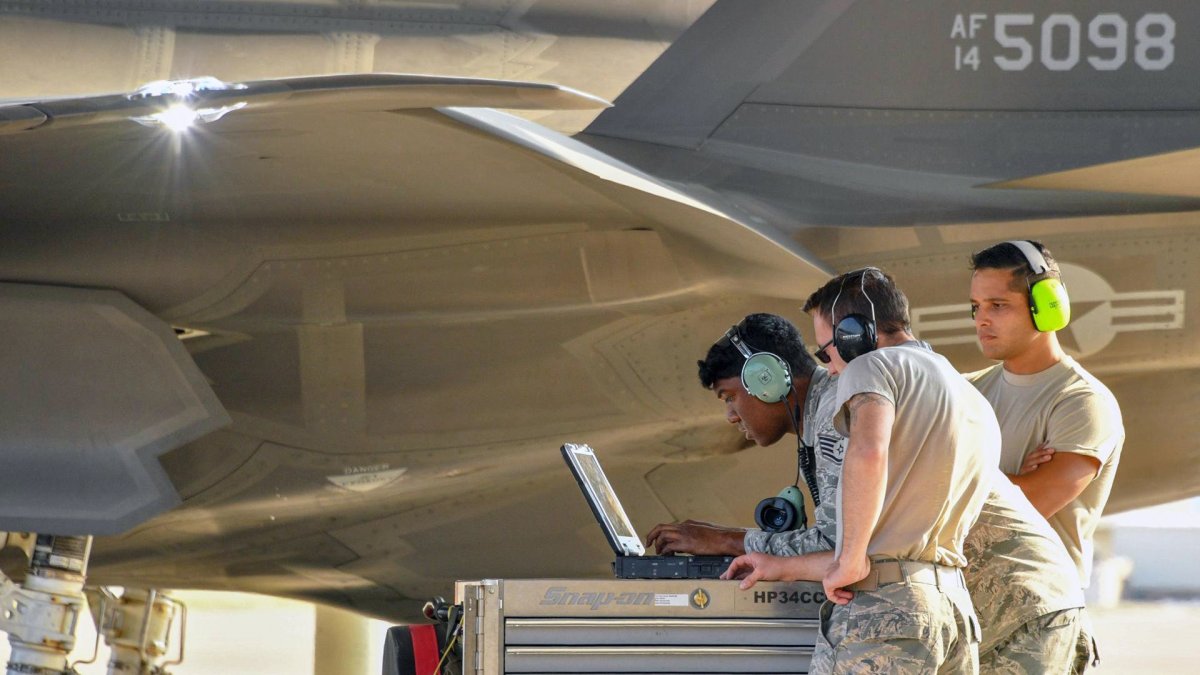
Tech. Sgt. Emil Wodicka, left, and Staff Sgt. Samantha Birnschein, 372nd Training Squadron, Detachment 3, work a wing reattachment and repair on a repurposed F-35A Lightning II at Hill Air Force Base, Utah, July 13, 2020., U.S. Air Force photo by R. Nial Bradshaw
It is impossible to assure every aspect of the enterprise against sophisticated and dedicated state attackers all the time. Therefore, the best defense against a potentially crippling cyberattack targeting key air assets in wartime might well be to increase the level of redundancy and extra capacity in the maintenance and spares system to reduce the impact of attacks when they inevitably occur. This would also have significant potential benefits in terms of improving overall availability but as always, the limiting factor that constrains such ‘inefficiency’ in peacetime is cost.
In terms of real-time cyber enablers for conventional operations, the first key question for air forces is what enemy systems have been infiltrated and implanted with relevant cyber payloads capable of causing operationally useful effects? If the conflict in question is against an adversary nation or in an area that was not a major focus for defense planners prior to the outbreak of hostilities, then it is unlikely that cyber payloads are already in place. Given the time scales required to develop and successfully install them, cyber professionals cannot simply create operationally relevant effects from scratch at short notice. However, critical assets such as the air defense networks of well-established adversary nations are likely to have been the target of longer-term efforts, and there may be useful payloads in place either in the main systems themselves or within ancillary systems upon which they depend.
Cyberweapons have a very different development and use profile than kinetic weapons., USAF
The second question at that point is whether the officers planning an airstrike at the operational level are aware that the potentially useful cyber capability exists or not. Offensive cyber capabilities are some of the most highly classified national security tools. Even if planners are aware of the existence of a potentially useful cyber capability, they may well lack the authority to authorize their use in support of conventional strike operations. High-end cyber payloads embedded within important components of a state adversary’s defenses take years to develop and emplace, and once used will be rapidly discovered, patched out, and potentially attributed. The adversary will also gain detailed knowledge about the techniques employed as they examine the code within the payload, which could help them improve their own offensive cyber capabilities over time. Therefore, the authority to use them will be vested at a very senior level, most likely head of state or at least Joint Chiefs level.
If the capability is known and can be authorized in sufficient time to be incorporated into the planning process for a conventional air operation, the third vital question is whether it can be coordinated sufficiently closely with the precise timings of aircraft movements and weapons releases.
The emergence of Active Electronically Scanned Array (AESA) radars as a primary sensor and emitter on modern combat air platforms does offer a potential way to remotely trigger previously emplaced cyber payloads in enemy systems. Since any radar must be, by its very nature, a receiver that transmits an interpretation of electronic signals as encoded data into a network, AESA radars can be used to interact with enemy air defenses in a more sophisticated manner than traditional EW.
An AN/APG-79 AESA being fitted into a F/A-18 Legacy Hornet., Raytheon
With a sufficiently detailed understanding of an enemy radar system and the way it interacts with the wider defense network, airborne AESA radars could be used to either transmit coded activation signals for a previously emplaced cyber payload, or electromagnetic energy patterns designed to be recognized as a trigger signal by the payload when they are picked up by the hostile radar.
However, bearing in mind the difficulties in assuring remote triggering access and proper functioning of a previously installed cyber payload in an enemy system, any air operation which includes cyber enablers must accept a significant risk that the cyber capability does not work as expected. Furthermore, once used, an adversary will quickly dig out and identify the code in question, so cyber payloads – while potentially capable of causing significant disruption at key moments – tend to be single-shot weapons with temporary effects.
In the air domain, cyber weapons are best thought of as tools that can help open a temporary window of vulnerability for a major strike force, given sufficient preparation time, permissions, and understanding across multiple command levels. The challenge they pose to air forces is primarily a persistent disruptive threat to information security, ancillary systems, and logistics chains. For rapid, on-demand degradation of key enemy sensors and weapons systems, however, kinetic strikes and digitally-enabled electronic warfare remain far more important.
Justin Bronk is a Research Fellow for Airpower at RUSI
Comments couldn’t be loaded. Please refresh the page.
更新于美国东部时间2021年8月18日下午6:03
在政策和军事领域,“网络”一词已变得相对普遍,它既是传统空军能力面临的威胁,也是其增强手段。网络武器无疑是战争、间谍活动和威慑的重要工具。随着社会结构日益数字化和网络化,网络武器的潜在攻击面也在迅速扩大。然而,非专业人士常常误解军用级网络能力的开发和部署流程的节奏和性质。对进攻性电子战和网络能力之间界限的混淆,会进一步扭曲公众对这些重要能力如何融入常规军事行动,尤其是空军运用方式的讨论。
总体而言,电子战(EW)和网络战之间的根本分界线在于:进攻性电子战能力旨在利用电磁能量辐射与敌方系统进行交互,而进攻性网络战能力旨在利用代码形式的数据与敌方系统进行交互。然而,在实践中,这两个作战领域的界限往往较为模糊。尤其值得注意的是,越来越多的平台,例如美国海军的EA-18G“咆哮者”电子战飞机和F-35“闪电II”战斗机,都配备了能够同时使用电子战和网络战技术与敌方系统交互的系统和传感器,并且在某些情况下,还能在飞行中快速地在两种技术之间切换。
两者也有相似之处,例如,设计有效的军事电子战和网络战能力都需要对目标系统或网络有深入的了解,而且这种了解必须经常更新才能保持有效性。然而,开发针对军事系统的电子攻击能力和进攻性网络能力所需的时间却截然不同。这是因为网络攻击的运作方式不同。
EA-18G 是一款电子战平台,但其任务也可能延伸至网络空间。(美国海军中校伊恩·C·安德森摄)
军事网络攻击的本质是通过访问、篡改或删除敌对网络中存储的数据来实现的。这种攻击在虚拟领域进行,旨在对现实世界产生影响。因此,网络攻击的目的多种多样,取决于所访问的数据及其在宿主网络和/或系统中的预期功能。成功攻击的影响范围很广,包括获取有关威胁系统工作原理的详细情报、阻止目标系统正常运行、暂时禁用关键功能,甚至导致系统故障并造成物理损坏。
本文由 Private Internet Access 赞助。
然而,在网络攻击有效载荷中实现任何预期效果之前,攻击者必须先弄清楚敌方网络中存储了哪些数据,以及这些网络使用了哪些编程语言和编程逻辑。许多民用网络使用市面上常见的、因此易于理解的编程语言和逻辑。这使得渗透并利用此类系统比渗透专门设计且受到定期监控的敏感军事系统要容易得多。无论哪种情况,网络攻击者都必须先获得初始接入点,然后才能发现并提取数据,从而揭示特定网络上存储的内容及其编码方式。
美国军方正竞相研发网络武器并防御此类武器。(美国空军)
策划任何网络攻击的第一步至关重要,必须在不被识别为敌对行为的情况下完成数据泄露。对于定制的军事系统而言,由于攻击者最初并不熟悉网络的编程语言和规则,因此这项任务更加困难,他们很难很好地模仿合法的网络流量以避免被快速发现。
如果检测到攻击者,他们不仅会被迅速隔离出网络,还可能遭到利用其创建的网关连接的反击。最敏感的军事系统通常也采用物理隔离,这意味着它们没有任何与外部网络或互联网的接口,无论是有线还是无线接口。因此,为了进行初步的网络侦察,攻击者需要绕过物理隔离措施,然后建立远程访问连接,以便窃取数据并进行后续的渗透尝试。
一旦确定某个网络包含可供窃取、篡改或删除的有用目标数据,攻击者就必须尝试绕过安全措施,并获取管理员帐户的控制权,从而获得必要的权限。由于几乎所有军事和敏感的民用系统都受到多因素身份验证安全措施的保护,这意味着攻击者要么需要情报人员自愿或被迫交出密码、密钥和生物识别信息,要么需要通过黑客攻击来绕过这些安全措施。
在马里兰州米德尔河沃菲尔德空军国民警卫队基地的“猎人巢穴”内,一名网络战作战军官正在观察第175网络空间作战大队的成员分析日志文件,并利用Kibana可视化工具在大型数据墙上提供网络威胁更新信息。(JM Eddins Jr./美国空军)
黑客攻击是指寻找网络代码中的歧义或错误,并利用这些漏洞绕过身份验证信息的输入。大多数复杂系统都存在潜在漏洞,但敏感网络也会定期进行检查和修补,以消除任何偶然发现或因检测到的攻击而暴露的漏洞。
一旦攻击者获得对所需管理节点的访问权限,他们就可以利用这些节点篡改和植入数据,包括网络武器。网络武器是一段代码包,通常经过精心校准,可在特定的网络系统中执行特定功能,同时尽可能地增加防御者追踪和检测的难度。网络有效载荷一旦成功植入,即可立即触发。但是,如果计划在未来使用,则必须将其编码为在满足特定条件时自动触发;否则,必须重新建立访问权限,才能在所需的时间点触发。
许多军事系统在对抗现代敌对势力时,会长时间处于辐射控制状态。对于舰船、移动式地对空导弹系统和飞行中的飞机而言,它们还与大多数潜在的入侵手段进行了物理隔离。此外,软件也会定期更新和修补,这使得用于入侵的漏洞能够在网络武器的有效载荷被触发之前被有意或无意地关闭。
S-400防空系统控制元件,俄罗斯国防部
软件更新也可能改变系统的内部逻辑,导致先前部署的网络能力在被触发时无法按预期运行。此外,军用网络通常通过对有限数量的已知接入点上的所有流量进行实时监控来保护。因此,每次试图触发、确认或更新已部署的网络武器能力的访问尝试都存在被网络防御者发现并随后被清除或反击的风险。
实际情况是,针对敌方敏感军事资产(例如防空预警网络、飞机航电系统或情报处理系统)开发网络攻击能力需要数年集中精力,并且存在被发现和归因的重大风险。此外,即使该能力建立起来,也无法保证它能够按需启动以支持未来的军事行动,也无法保证它不会在使用前被敌方网络防御系统发现或修复而失效。
如果有效载荷逃逸到其设计攻击目标系统之外,则无法准确预测可能产生的各种二阶和三阶效应。因此,大多数国家将此类能力视为战略级军事工具,对其存在、能力和局限性的了解都属于极高的机密级别。其发布授权通常也需要比传统军事资产更高级别的军事和政治指挥机构批准。
在敏感的敌对网络中建立能力所需的时间,以及部署有效载荷的保障和触发难度,都会显著影响网络能力与空中领域的互动方式。从中长期来看,网络能力最重要的用途之一是收集有关敌方关键系统的敏感信息,例如雷达、导弹制导逻辑或导引头性能。此类数据对于编写有效的飞机对抗系统、电子战系统、优化末端导弹规避战术等至关重要。
一架F-35原型机在消声室中进行电磁测试。(洛克希德·马丁公司-杰克·诺布尔)
公开承认的旨在获取美国空军系统此类信息的网络安全攻击表明,大多数国家级攻击的目标是工业供应链,而非定制的军事系统。这合乎情理,因为许多现代空战和空战武器项目的供应链都是跨国且多元化的,这使得攻击者更容易找到漏洞和安全措施松懈的网络。这也预示着未来冲突中,作战空中能力可能更容易遭受直接网络攻击。
大多数航空电子设备和任务系统都处于封闭且受到严密监控的状态,这使得敌方在实践中很难(尽管并非完全不可能)直接对飞机和指挥系统发起网络攻击。然而,如果防御力度较弱的辅助后勤和工业供应网络在未来国家间冲突的关键阶段,由于先前植入的敌方网络载荷而突然出现故障或失效,也并不令人意外。
如果备件供应不稳定,即使是最简单的作战飞机也会迅速失去效能,因为为了维持数量不断减少的可用战机,机队不得不拆解其他机型进行维修。如果弹药和燃料供应中断,作战效能和出动率的下降速度会更快。随着西方空军所依赖的供应链和维护体系数字化程度的不断提高,潜在的攻击面也在不断扩大。
2020年7月13日,在犹他州希尔空军基地,第372训练中队第3分队的技术军士埃米尔·沃迪卡(左)和参谋军士萨曼莎·伯恩沙因正在对一架改装的F-35A“闪电II”战斗机进行机翼重新安装和维修。(美国空军照片,R·尼尔·布拉德肖摄)
要时刻确保企业各个方面免受老练且专业的国家级攻击者的侵害是不可能的。因此,在战时,针对关键空中资产可能造成严重破坏的网络攻击的最佳防御措施,或许是提高维护和备件系统的冗余度和额外容量,从而降低攻击发生时的影响。这样做在提高整体可用性方面也具有显著的潜在优势,但一如既往,限制这种“低效”措施在和平时期应用的根本因素是成本。
就用于常规作战的实时网络赋能技术而言,空军面临的首要关键问题是:敌方哪些系统已被渗透并植入了能够产生实际作战效果的相关网络载荷?如果冲突对象是敌对国家,或者冲突发生在战前国防规划者并非重点关注的地区,那么网络载荷不太可能已经部署到位。考虑到开发和成功部署这些载荷所需的时间,网络专家无法在短时间内凭空创造出具有作战意义的效果。然而,对于实力雄厚的敌对国家的防空网络等关键资产,网络攻击很可能是长期行动的目标,其主要系统本身或其依赖的辅助系统中可能已经部署了有效的网络载荷。
网络武器的研发和使用方式与动能武器截然不同。——美国空军
第二个问题是,负责作战层面空袭计划的军官是否意识到潜在有效的网络攻击能力的存在。进攻性网络攻击能力属于最高机密的国家安全工具。即使计划人员意识到潜在有效的网络攻击能力的存在,他们也可能缺乏授权将其用于支持常规打击行动的权限。嵌入敌方国家防御系统重要组件中的高端网络载荷需要数年时间开发和部署,一旦使用,就会迅速被发现、修复,并可能被追溯到攻击者。敌方在检查载荷代码的过程中,还会获得有关所用技术的详细信息,这可能有助于他们随着时间的推移改进自身的进攻性网络攻击能力。因此,使用这些能力的授权将授予极高层,很可能是国家元首,或者至少是参谋长联席会议级别。
如果已知该能力,并且能够及时获得授权以便将其纳入常规空中作战的计划过程中,那么第三个关键问题是,它能否与飞机移动和武器投放的精确时间进行足够紧密的协调。
有源相控阵雷达(AESA)作为现代作战空中平台的主要传感器和发射器,其出现为远程触发敌方系统中预先部署的网络攻击载荷提供了一种潜在途径。由于任何雷达本质上都必须是接收器,并将对电子信号的解读以编码数据的形式传输到网络中,因此AESA雷达可以比传统电子战更复杂地与敌方防空系统进行交互。
雷神公司正在将AN/APG-79有源相控阵雷达安装到F/A-18“大黄蜂”战斗机上。
通过对敌方雷达系统及其与更广泛的防御网络交互方式的足够详细的了解,机载有源相控阵雷达可以用于发射编码激活信号,以激活先前部署的网络有效载荷;或者发射电磁能量模式,当敌方雷达接收到这些模式时,这些模式会被有效载荷识别为触发信号。
然而,考虑到确保远程触发权限以及预先安装在敌方系统中的网络载荷正常运行的难度,任何包含网络作战能力的空中行动都必须承担网络能力无法按预期发挥作用的重大风险。此外,一旦使用,敌方会迅速挖掘并识别相关代码,因此,网络载荷虽然有可能在关键时刻造成重大干扰,但通常属于一次性武器,其效果也较为短暂。
在空中领域,网络武器最好被视为一种工具,在充足的准备时间、授权以及各级指挥机构的充分理解下,可以帮助主力打击部队打开一个暂时的脆弱窗口。它们对空军构成的挑战主要在于对信息安全、辅助系统和后勤链的持续性破坏性威胁。然而,若要快速、按需地削弱敌方关键传感器和武器系统,动能打击和数字化电子战仍然更为重要。
Justin Bronk 是 RUSI 空中力量研究员
评论加载失败,请刷新页面。