Volt Typhoon hacks likely to inspire copycats, CNMF’s Mahlock saysCNMF的马洛克表示,Volt Typhoon的破解事件可能会引发模仿者。
Attacks on critical infrastructure — food and water delivery, health care services, defense contracting and more — could hamper U.S. military response.
The Volt Typhoon hacks that targeted U.S. critical infrastructure won’t be the last of their kind, according to a Marine Corps cyber leader.
The Chinese intrusion affected organizations spanning the communications, utilities, education and government sectors including in Guam, a key foothold for American forces in the Indo-Pacific. The incident was disclosed in May 2023, with Microsoft describing the years-long operation as hard to detect and malicious.
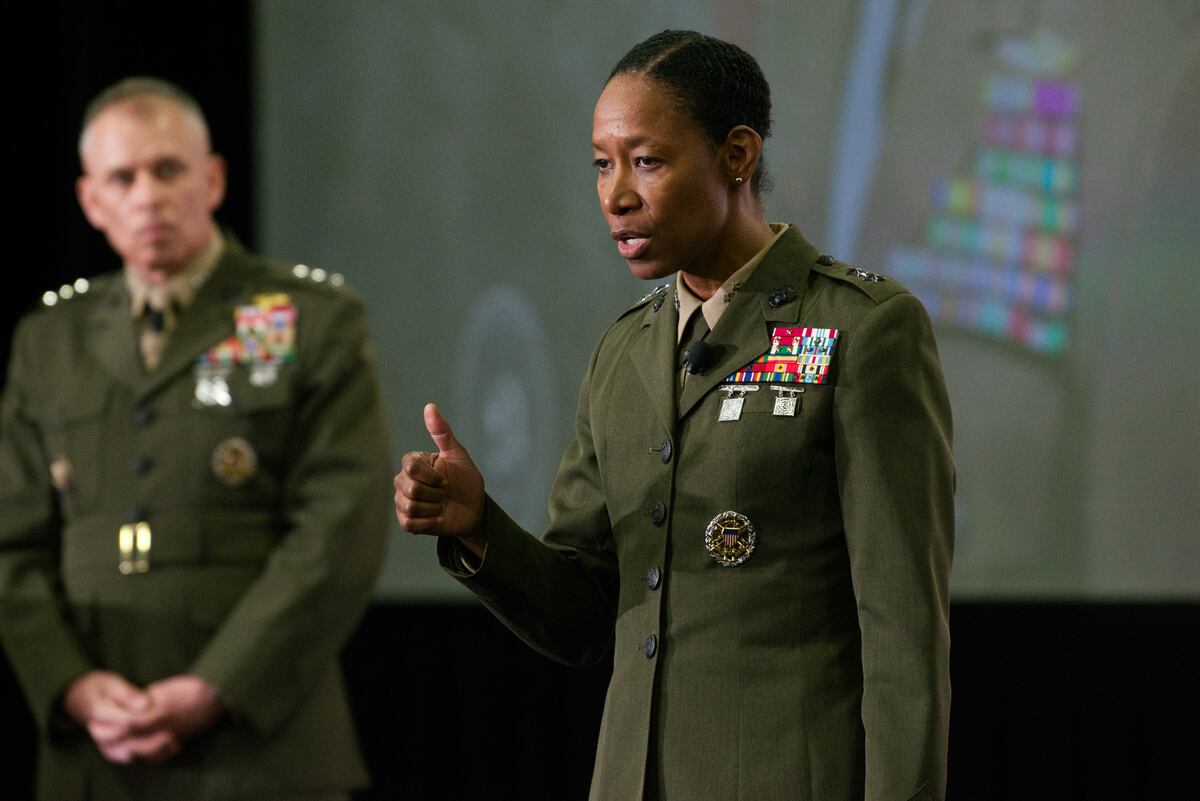
The attack is likely to inspire copycats, said Maj. Gen. Lorna Mahlock, the commander of the Cyber National Mission Force. The CNMF, part of Cyber Command, deploys around the world to unearth malware and fortify digital defenses.
“I think we’re seeing Volt Typhoon activity continuing to persist. That’s in open source. We’re also seeing other actors using the tactics, techniques and procedures,” Mahlock said April 30 at the Modern Day Marine defense conference in Washington. “The greatest form of flattery is to copy.”
U.S. officials have long considered China a serious cyber hazard, with the International Institute for Strategic Studies think tank placing it in the second tier of its cyber powerhouse rankings alongside Russia. The Pentagon’s 2023 cyber strategy warned both Beijing and Moscow are prepared to unleash cyberattacks on critical infrastructure and defense networks should war break out.
The groundwork is being laid today. Volt Typhoon relied on so-called living-off-the-land techniques to lurk around vital systems and go largely unnoticed.
Attacks on critical infrastructure — food and water delivery, health care services, defense contracting and more — could jeopardize U.S. military response across the world as well as a sense of stateside calm. A ransomware attack on Colonial Pipeline in 2021 resulted in a run on fuel across the Southeast and aggravated concerns about energy security.
“Open-source reporting talks about this actor, out of China, who has access to our critical infrastructure and some of our key capabilities. Why? Not just for foreign intelligence-collection,” Mahlock said.
“We’ve seen this actor, China , grow in scope, scale and sophistication,” she added. “We’ve also seen that they’re undeterred.”
Colin Demarest was a reporter at C4ISRNET, where he covered military networks, cyber and IT. Colin had previously covered the Department of Energy and its National Nuclear Security Administration — namely Cold War cleanup and nuclear weapons development — for a daily newspaper in South Carolina. Colin is also an award-winning photographer.
一位海军陆战队网络指挥官表示,针对美国关键基础设施的“伏特台风”黑客攻击不会是此类攻击的最后一次。
此次中国入侵事件影响了包括关岛在内的多个机构,涵盖通信、公用事业、教育和政府等多个领域。关岛是美国在印太地区的重要据点。该事件于2023年5月披露,微软称此次持续数年的行动难以检测且恶意。
网络国家任务部队指挥官洛娜·马洛克少将表示,此次攻击很可能引发模仿者。网络国家任务部队隶属于网络司令部,其任务遍及全球,旨在发现恶意软件并加强网络防御。
“我认为我们看到Volt Typhoon的活动仍在持续。这是开源的。我们也看到其他行动者在使用类似的战术、技术和程序,”马洛克4月30日在华盛顿举行的现代海军陆战队防御会议上说。“最高的赞美莫过于模仿。”
美国官员长期以来一直将中国视为严重的网络威胁,国际战略研究所(ISS)智库已将其与俄罗斯并列为网络实力第二梯队。五角大楼2023年网络战略警告称,一旦战争爆发,北京和莫斯科都已做好准备,对关键基础设施和国防网络发动网络攻击。
今天,一切准备工作都已就绪。伏特台风依靠所谓的“就地取材”技术潜伏在重要系统周围,并且几乎不被人察觉。
对关键基础设施(包括食品和饮用水供应、医疗保健服务、国防承包等)的攻击可能会危及美国在全球范围内的军事反应能力,并破坏美国国内的平静。2021年,科洛尼尔输油管道公司(Colonial Pipeline)遭受勒索软件攻击,导致美国东南部地区出现燃料抢购潮,并加剧了人们对能源安全的担忧。
“开源报道提到,有一位来自中国的行动者能够接触到我们的关键基础设施和一些关键能力。为什么?不仅仅是为了收集外国情报,”马洛克说。
她补充说:“我们看到中国这个角色在范围、规模和成熟度上不断增长。我们也看到他们毫不气馁。”
科林·德马雷斯特曾是C4ISRNET的记者,负责报道军事网络、网络安全和信息技术方面的新闻。此前,他曾为南卡罗来纳州的一家日报报道美国能源部及其下属的国家核安全管理局,主要关注冷战后的清理工作和核武器研发。科林还是一位屡获殊荣的摄影师。