MoneySmart data breach hits customers in Singapore and Hong Kong; IC numbers, financial info exposedMoneySmart数据泄露事件波及新加坡和香港客户;身份证号码和财务信息泄露
MoneySmart says data breach affected customers in Singapore and Hong Kong after hackers accessed internal systems. Read more at straitstimes.com.
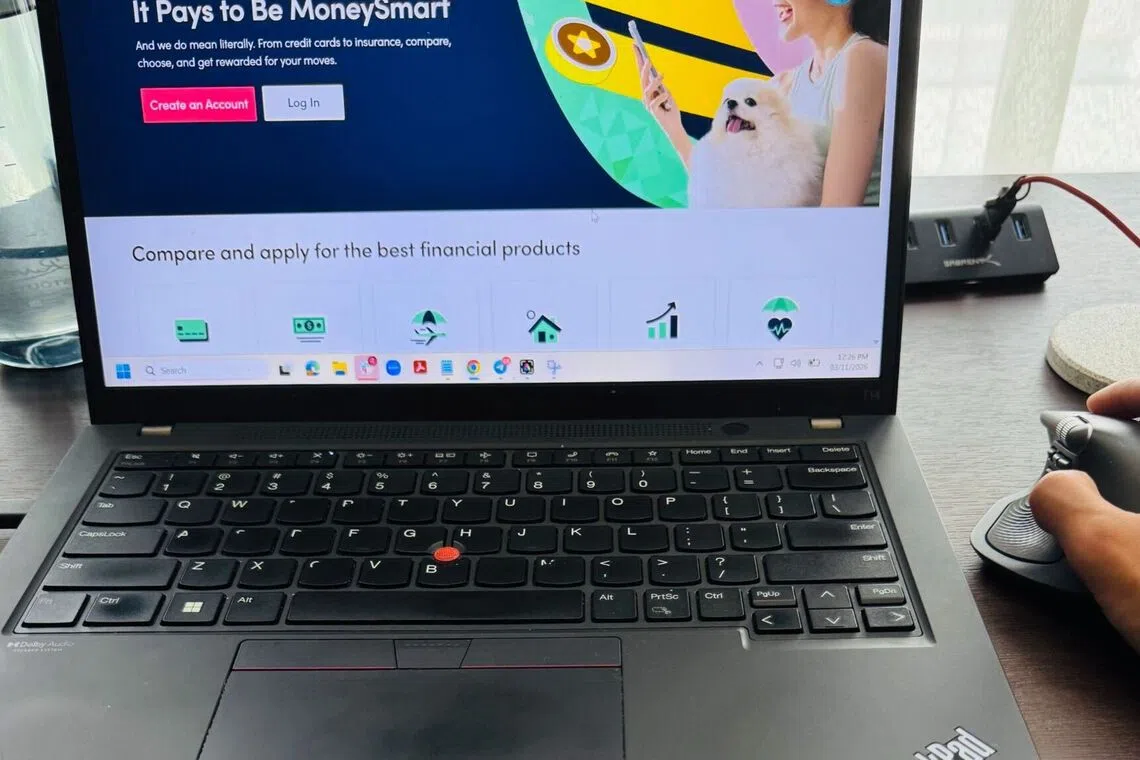
MoneySmart operates an online platform that allows consumers to evaluate, compare and purchase products.
Published Nov 03, 2026, 01:03 PM
Updated Nov 03, 2026, 01:03 PM
SINGAPORE – The personal data of some MoneySmart customers in Singapore and Hong Kong has been compromised after hackers breached the personal finance portal ’s internal IT systems in October.
In an e-mail sent to affected users on Nov 2 and 3 and seen by The Straits Times, the platform said an unauthorised third party gained access to some of its internal information technology systems on Oct 29.
“These systems hold personal data that customers share with us when they compare or apply for financial products through MoneySmart,” it said.
MoneySmart’s online platform allow consumers to evaluate , compare and apply for financial products, including credit cards, personal loans and travel insurance .
In response to queries from The Straits Times on Nov 3, the company confirmed that personal data belonging to some customers in Singapore and Hong Kong was copied.
Customer details that were potentially accessed include:
Personal particulars: Names, dates of birth, nationality and personal identification numbers
Contact information: E-mail addresses and mobile numbers
Financial profiles: Income ranges, life stages, and financial products currently owned
Vehicle and insurance details: Vehicle information, car insurance enquiries or policies
The company is contacting customers impacted by the breach directly to explain what data was involved and recommend steps they can take to protect themselves.
“As soon as we discovered the incident, we stopped the unauthorised access and took steps to secure our systems,” MoneySmart chief executive officer Vinod Nair said.
Regulators in both markets have been alerted, including the Personal Data Protection Commission (PDPC) and the Monetary Authority of Singapore (MAS), alongside the Office of the Privacy Commissioner for Personal Data and the Insurance Authority in Hong Kong.
Independent cybersecurity and digital forensics experts have been hired to investigate the breach, the company added.
Meanwhile, MoneySmart emphasised that its operations continue as normal.
“MoneySmart continues to operate as normal, and we are committed to supporting our customers,” said MoneySmart’s Nair.
“We are reviewing everything that led to this incident and making the changes needed to prevent it from happening again,” he added.
“I am deeply sorry to everyone affected,” said Nair. “Customers trust us with information about their financial lives, and we take that responsibility very seriously.”
ST has contacted MoneySmart, PDPC, MAS, the Cyber Security Agency of Singapore and the police for more information.
Personal Data Protection Act
MoneySmart运营着一个在线平台,允许消费者评估、比较和购买产品。
发布于 2026 年 11 月 3 日下午 1:03
更新于2026年11月3日下午1:03
新加坡——今年10月,黑客入侵了个人理财门户网站MoneySmart的内部IT系统,导致新加坡和香港部分MoneySmart客户的个人数据遭到泄露。
《海峡时报》看到的一封于 11 月 2 日和 3 日发送给受影响用户的电子邮件中,该平台表示,未经授权的第三方于 10 月 29 日访问了其部分内部信息技术系统。
“这些系统保存着客户通过 MoneySmart 比较或申请金融产品时与我们分享的个人数据,”该公司表示。
MoneySmart 的在线平台允许消费者评估、比较和申请金融产品,包括信用卡、个人贷款和旅行保险。
针对《海峡时报》11月3日的询问,该公司证实,新加坡和香港部分客户的个人数据遭到复制。
可能被访问的客户信息包括:
个人信息:姓名、出生日期、国籍和个人身份证号码
联系方式:电子邮件地址和手机号码
财务概况:收入范围、人生阶段和目前持有的金融产品
车辆及保险详情:车辆信息、汽车保险咨询或保单
该公司正在直接联系受此次数据泄露事件影响的客户,解释涉及哪些数据,并建议他们可以采取哪些措施来保护自己。
MoneySmart 首席执行官 Vinod Nair 表示:“我们一发现该事件,就立即停止了未经授权的访问,并采取措施保护我们的系统。”
新加坡和新加坡的监管机构均已接到通知,包括新加坡的个人资料保护委员会 (PDPC) 和新加坡金融管理局 (MAS),以及香港的个人资料私隐专员公署和保险业监管局。
该公司补充说,已聘请独立的网络安全和数字取证专家对此次数据泄露事件进行调查。
与此同时,MoneySmart强调其运营一切照常。
MoneySmart 的 Nair 表示:“MoneySmart 将继续正常运营,我们将致力于为客户提供支持。”
“我们正在审查导致这起事件的所有因素,并做出必要的改变,以防止此类事件再次发生,”他补充道。
“我对所有受影响的人深表歉意,”奈尔说。“客户信任我们,将他们的财务信息托付给我们,我们非常重视这份责任。”
《海峡时报》已联系MoneySmart、PDPC、新加坡金融管理局、新加坡网络安全局和警方以获取更多信息。
个人数据保护法