No way to tell if S’pore investors affected by Binance hack; withdrawals temporarily suspended无法确定新加坡投资者是否受到币安黑客攻击的影响;提现功能已暂时暂停
Binance hack: no way to tell if Singapore investors were affected, with withdrawals suspended during a security overhaul. Read more at straitstimes.com.
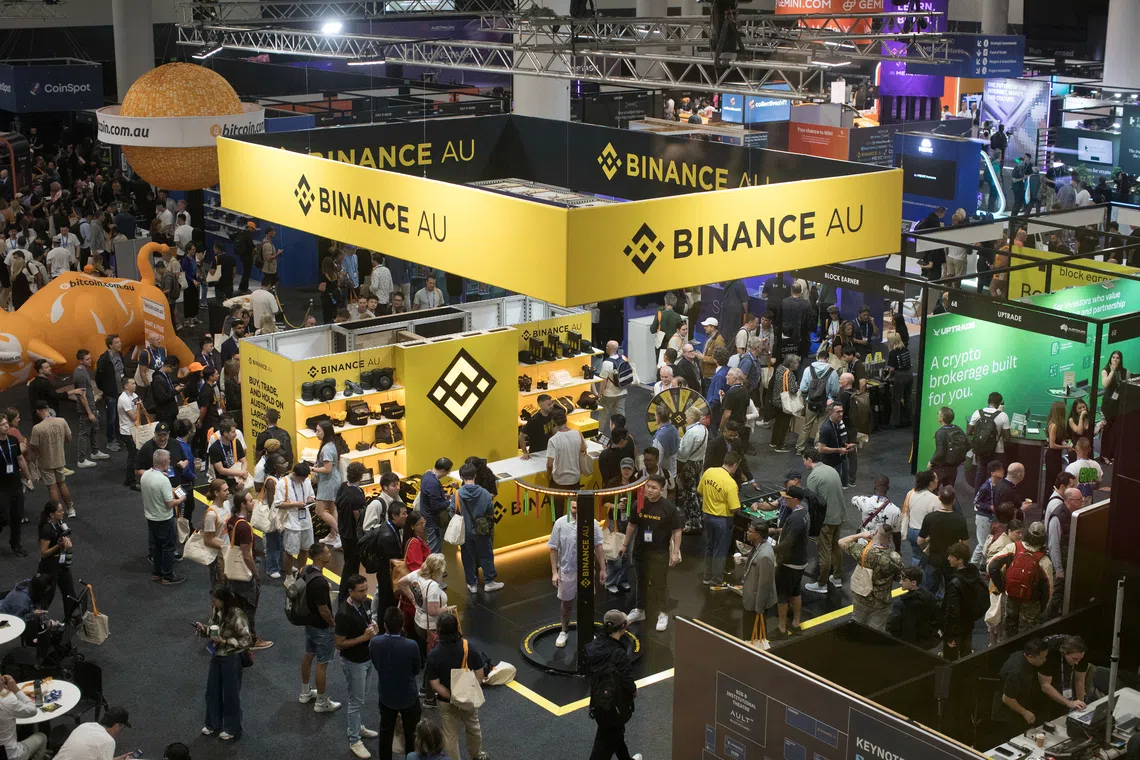
The hack involved around US$6.3 billion (S$8 billion) in funds.
Published Oct 30, 2026, 07:42 PM
Updated Oct 30, 2026, 11:48 PM
SINGAPORE – There is no way to determine whether any Singapore-based funds or investors were affected by a multibillion-dollar hack on cryptocurrency exchange Binance, or how much may have been stolen from them.
However, withdrawals from the exchange will remain suspended until a security overhaul is completed, The Straits Times has learnt. User funds remain safe and deposits unaffected.
In response to queries by ST on Oct 30, Ari Redbord, head of global policy at blockchain investigation firm TRM Labs, said the funds involved were held in centralised hot wallets, meaning they cannot be traced to individual investors or jurisdictions based on blockchain data alone.
Centralised hot wallets are internet-connected digital wallets managed by cryptocurrency exchanges to hold and transfer funds on behalf of customers.
As funds belonging to different customers may be pooled together, blockchain data alone cannot identify which investors or countries the funds are linked to. But crypto exchanges themselves may have records that could help identify the affected customers.
“Hot wallets are not untraceable, rather they operate like bank vaults... If someone robbed a bank and took money from the vault, you would say the bank was robbed,” said Redbord.
“It would not affect any specific customer’s balance.”
When contacted, Binance told ST that deposits are unaffected, but withdrawals will remain paused while it “completes a security revamp of the withdrawal service and its related addresses”.
The cryptocurrency platform said on Oct 29 that it had been hit by a hack involving around US$6.3 billion (S$8 billion) in funds, about half of which had been frozen to prevent further losses.
When asked whether any Singapore-based funds or investors were affected, Binance said it was “continuing to actively investigate” and, “as a matter of policy”, does not comment on individual funds or investors.
But it added that user funds were safe and that it would publish an updated proof of reserves once remedial measures were completed.
The amount taken in the hack on Oct 29 was more than four times the US$1.5 billion stolen from cryptocurrency exchange Bybit in February 2025, which was then the largest cryptocurrency heist on record.
The Bybit attack was attributed to TraderTraitor, a hacking group linked to North Korea.
The hackers moved quickly to launder the stolen Ether, converting much of it into Bitcoin and routing funds through decentralised exchanges and other services to obscure their trail. Bybit later covered the US$1.5 billion shortfall with emergency loans and liquidity support from its partner firms.
TRM Labs said on Oct 29 that it had “high confidence” the same group was behind the Binance hack, based on intelligence gathered from blockchain transactions and other sources.
The Monetary Authority of Singapore (MAS) placed Binance.com, the trading platform operated by Binance, on its Investor Alert List in September 2021 to warn consumers that it was not regulated or licensed to provide payment services in Singapore.
The regulator also ordered Binance to stop providing payment services in Singapore and cease soliciting business from Singapore residents.
In December that year, Binance Asia Services, Binance’s Singapore affiliate, withdrew its application for a licence from MAS to provide digital payment token services here.
Binance said at the time that its Singapore affiliate would instead focus on becoming a blockchain innovation hub to support the development of the global blockchain ecosystem.
Binance.com remains on MAS’ Investor Alert List as at Oct 30.
Monetary Authority of Singapore
此次黑客攻击涉及金额约63亿美元(80亿新元)。
发布于 2026 年 10 月 30 日晚上 7:42
更新于2026年10月30日晚上11:48
新加坡——目前尚无法确定是否有任何新加坡基金或投资者受到加密货币交易所币安数十亿美元黑客攻击的影响,也无法确定他们可能被盗走了多少资金。
据《海峡时报》报道,交易所的提款功能将继续暂停,直至安全系统升级完成。用户资金安全无虞,存款不受影响。
针对《海峡时报》10 月 30 日的询问,区块链调查公司 TRM Labs 的全球政策主管 Ari Redbord 表示,涉案资金存放在集中式热钱包中,这意味着仅凭区块链数据无法追踪到个人投资者或司法管辖区。
集中式热钱包是由加密货币交易所管理的联网数字钱包,用于代表客户持有和转移资金。
由于不同客户的资金可能被汇集在一起,仅凭区块链数据无法识别这些资金与哪些投资者或国家/地区相关联。但加密货币交易所本身可能拥有有助于识别受影响客户的记录。
“热钱包并非无法追踪,而是像银行金库一样运作……如果有人抢劫了银行并从金库中拿走了钱,你会说银行被抢劫了,”雷德博德说。
“这不会影响任何特定客户的账户余额。”
币安在接受ST采访时表示,充值不受影响,但提现将继续暂停,以便“完成提现服务及其相关地址的安全升级”。
该加密货币平台于 10 月 29 日表示,其遭受黑客攻击,涉及资金约 63 亿美元(80 亿新元),其中约一半已被冻结以防止进一步损失。
当被问及是否有任何新加坡基金或投资者受到影响时,币安表示“正在积极调查”,并且“根据政策”,不对个别基金或投资者发表评论。
但该公司补充说,用户资金是安全的,一旦补救措施完成,将公布更新后的储备金证明。
10 月 29 日的黑客攻击中被盗金额是 2025 年 2 月从加密货币交易所 Bybit 被盗的 15 亿美元的四倍多,而 Bybit 被盗的金额当时是史上最大的加密货币盗窃案。
Bybit 遭受的攻击被认为是与朝鲜有关联的黑客组织 TraderTraitor 所为。
黑客迅速采取行动,洗白窃取的以太币,将其中大部分兑换成比特币,并通过去中心化交易所和其他服务转移资金,以掩盖其踪迹。Bybit 后来通过紧急贷款和合作伙伴公司的流动性支持,弥补了 15 亿美元的资金缺口。
TRM Labs 于 10 月 29 日表示,根据从区块链交易和其他来源收集的情报,他们“高度确信”币安黑客事件是同一组织所为。
新加坡金融管理局 (MAS) 于 2021 年 9 月将币安运营的交易平台 Binance.com 列入投资者警示名单,以警告消费者该平台未获得新加坡的监管或许可提供支付服务。
监管机构还命令币安停止在新加坡提供支付服务,并停止向新加坡居民招揽业务。
同年 12 月,币安的新加坡子公司币安亚洲服务公司撤回了向新加坡金融管理局 (MAS) 申请在新加坡提供数字支付代币服务的牌照。
币安当时表示,其新加坡子公司将专注于成为区块链创新中心,以支持全球区块链生态系统的发展。
截至10月30日,Binance.com 仍位于新加坡金融管理局的投资者警示名单上。
新加坡金融管理局