46,000 SIA booking records accessed illegally in data breach affecting software provider Amadeus46,000 条新加坡航空 (SIA) 预订记录遭非法访问,数据泄露事件波及软件供应商 Amadeus。
Bank account or credit card information has not been exposed. Read more at straitstimes.com.
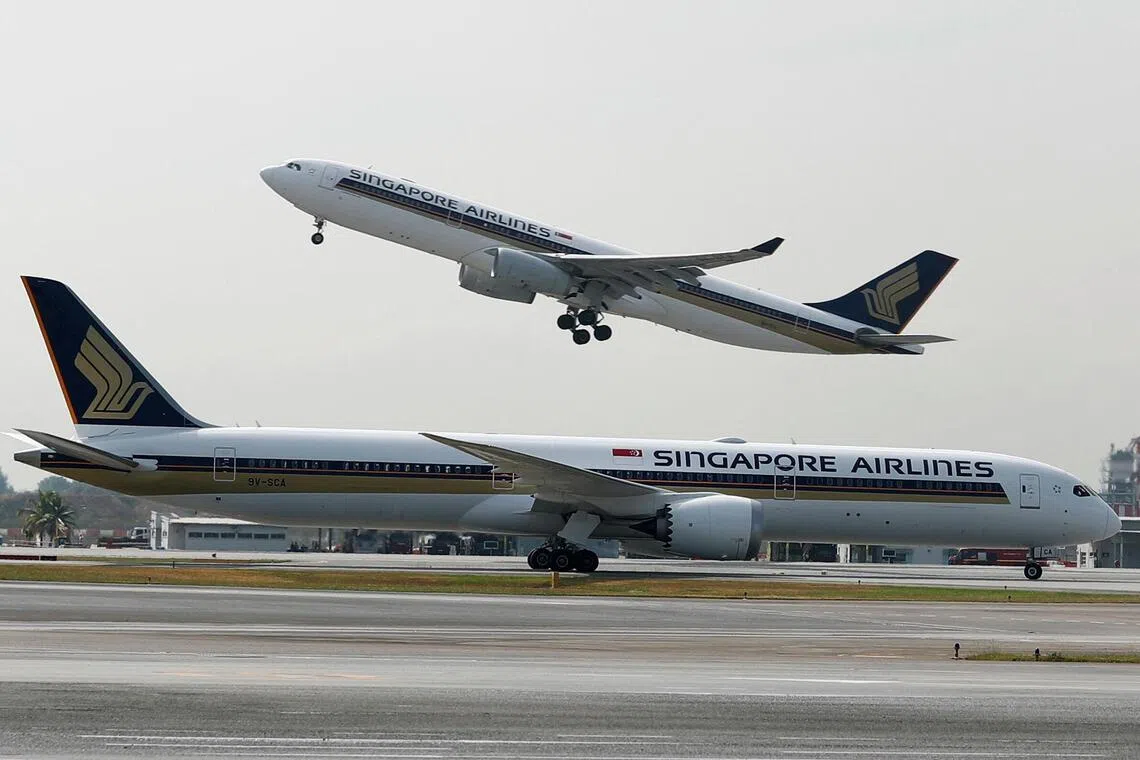
Data accessed included customers’ names, booking reference numbers, travel itineraries and booking classes.
Published Nov 03, 2026, 08:51 PM
Updated Nov 03, 2026, 08:51 PM
SINGAPORE – About 46,000 Singapore Airlines (SIA) booking records were affected by a data breach at the carrier’s reservation-technology provider, Amadeus.
In a media reply on Nov 3 , an SIA spokesperson said that data illegally accessed by a third party included customers’ names, booking reference numbers, travel itineraries and booking classes .
For about 620 booking records, information including e-mail addresses, phone numbers, travel document details, and KrisFlyer membership numbers may have been accessed , the spokesperson added.
However, Amadeus has confirmed that bank account or credit card information has not been exposed, and no booking has been modified, SIA said.
The incident was confined to Amadeus’ platform, and the global travel technology provider, which supports certain SIA reservations and booking processes , has told SIA that containment measures and additional security safeguards have been implemented following the breach , the airline said.
SIA said the incident did not involve a breach of its IT systems.
As a precaution, SIA said, it is directly contacting affected customers with upcoming travel to change their booking reference numbers.
SIA said it has also informed the relevant authorities about the matter.
“SIA sincerely apologises to affected customers for any inconvenience caused,” the spokesperson said.
“The protection of our customers’ personal data is of utmost importance to SIA.”
SIA joins a growing list of airlines that have reported customer data compromised in the Amadeus breach. These include Malaysia Airlines, Cathay Pacific Airways, Japan Airlines, South Korea’s Asiana Airlines, and others.
访问的数据包括客户姓名、预订参考编号、旅行行程和预订舱位等级。
发布于 2026 年 11 月 3 日晚上 8:51
更新于2026年11月3日晚上8:51
新加坡——新加坡航空公司(SIA)的预订技术提供商 Amadeus 发生数据泄露事件,导致约 46,000 条新加坡航空公司的预订记录受到影响。
11月3日,新加坡航空发言人在回复媒体时表示,第三方非法获取的数据包括客户姓名、预订参考编号、旅行行程和预订舱位等级。
发言人补充说,大约有 620 条预订记录的信息可能已被访问,其中包括电子邮件地址、电话号码、旅行证件详情和 KrisFlyer 会员号码。
新加坡航空公司表示,Amadeus 已确认银行账户或信用卡信息并未泄露,也没有任何预订被修改。
新加坡航空公司表示,此次事件仅限于 Amadeus 的平台。这家为新加坡航空部分预订流程提供支持的全球旅行技术提供商已告知新加坡航空,在发生此次安全漏洞后,已实施了遏制措施和额外的安全保障措施。
新加坡航空公司表示,该事件不涉及其IT系统遭到入侵。
新加坡航空公司表示,作为预防措施,他们正在直接联系受影响的、即将出行的乘客,更改他们的预订参考编号。
新航表示,已将此事告知相关部门。
“新加坡航空对由此给受影响的乘客带来的不便深表歉意,”发言人表示。
“保护客户的个人数据对新加坡航空公司来说至关重要。”
新加坡航空加入了越来越多报告客户数据在Amadeus数据泄露事件中遭到泄露的航空公司行列。这些航空公司包括马来西亚航空、国泰航空、日本航空、韩国韩亚航空等。