TRUST AS THE NEW COMPETITIVE ADVANTAGE IN MALAYSIA'S AI ECONOMY信任是马来西亚人工智能经济中新的竞争优势
MALAYSIAN organisations are moving quickly to put artificial intelligence (AI) to work.
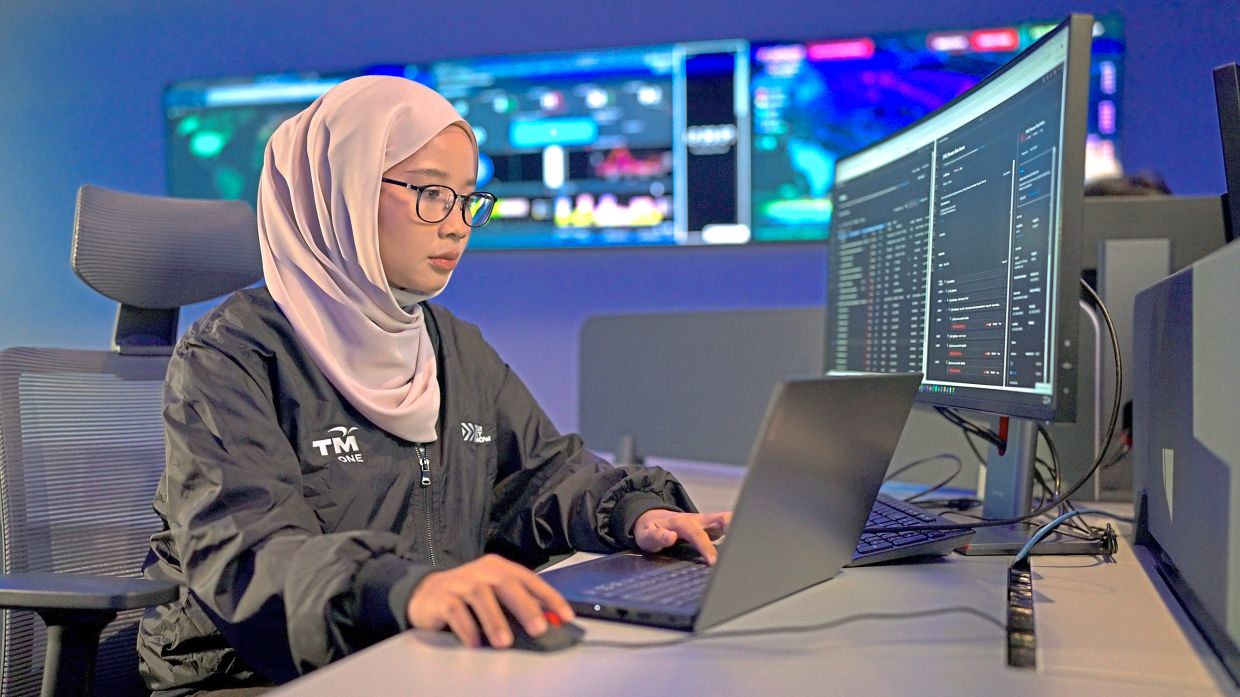
TM Cyber Defence Centre (CYDEC) is TM One’s next-generation security operations centre.
MALAYSIAN organisations are moving quickly to put artificial intelligence (AI) to work.
Boards are tracking use cases, productivity gains and time saved. One question receives far less attention: who is accountable when an AI system exposes sensitive information, makes the wrong decision or is manipulated by an attacker?
For TM One executive vice-president Shanti Jusnita Johari, closing that accountability gap must become a leadership priority.
As AI becomes embedded across operations, customer engagement and decision-making, accountability is emerging as one of the defining governance challenges facing boards today.
“Boards should not only ask how quickly AI can be deployed. They should ask whether the organisation can still keep its promises to customers and citizens when something goes wrong,” she says. “That is a leadership question.”
A mandate for boardrooms
Cybersecurity has moved from an IT line item to a boardroom mandate. Increasingly, boards must govern cyber and AI risks with the same discipline they apply to financial, operational and regulatory risks. As AI, cloud and automation become central to organisations, one incident can disrupt operations, weaken trust, interrupt supply chains and invite regulatory fallout.
Leaders therefore need to set clear accountability, define the organisation's tolerance for cyber risk and ensure continuity plans are tested, not merely documented.
“Cybersecurity isn't a cost centre. It's a condition for doing business with confidence,” Shanti explains. “Boards should ask for evidence that critical services can continue during an incident, not simply reassurance that security tools are in place.”
Malaysia's regulatory environment is also evolving alongside these risks. The Cyber Security Act 2024 places statutory obligations, including risk assessments, audits and incident notification, on National Critical Information Infrastructure operators, while the National Cyber Security Agency’s Malaysia Cyber Security Strategy 2025-2030 sets the country's five-year resilience roadmap.
The pace of adoption adds to the urgency. Within two years, the National AI Office evolved into AI Malaysia, a centralised apex agency steering the AI Nation 2030 ambition, including a Malaysian AI Safety Institute for model testing and red-teaming. In tandem, enterprise AI adoption has nearly doubled since 2020, according to the AIBP 2025/2026 AI Readiness Survey.
“These shifts reflect Malaysia's move to treat cyber resilience as a national imperative,” Shanti says. “For boards, that means making resilience a part of the AI agenda from the start, with clear ownership, investment and progress reviewed at leadership level.”
Shanti says that Malaysian enterprises are short of unified visibility that helps to identify risks and respond before they become major incidents.
Beyond reshaping efficiency, AI has changed the digital fight on both sides. Attackers can automate reconnaissance, generate phishing content and adapt faster than before. At the same time, organisations are accelerating AI adoption across operations, customer engagement and decision-making.
For leaders, the challenge is no longer simply deploying AI. Governance, visibility and accountability must evolve at the same speed.
For Shanti, one of AI's biggest effects is the compression of decision time. Threats can be identified, adapted and executed more quickly, while organisations themselves are becoming more interconnected and automated. The ability to see what is happening and act quickly is therefore becoming as important as the security technology itself.
Recent industry studies illustrate the growing cost and sophistication of cyber incidents. IBM's 2026 Cost of a Data Breach Report puts the global average breach cost at a record US$4.99mil, up 12% in a year, with AI-enabled attacks behind one in four malicious breaches.
Closer to home, Pikom's Beyond Compliance: The State of Cyber Resilience in Malaysia 2026 report found the average cost of a data breach in Malaysia climbed to RM3.2mil in 2025, up from RM2.9mil the year before, with some organisations reporting losses of more than RM5mil from a single incident. AI-generated phishing or deepfake impersonation now rank among the most common attacks Malaysian organisations face.
“The issue for leadership is decision speed,” she says. “Can the organisation see a threat early enough, understand its impact and make the right decision before the situation escalates? Buying more tools does not automatically give you that capability.”
TM CYDEC provides integrated end-to-end cybersecurity services, including 24/7/365 cyber threat monitoring and active defence.
The gap TM CYDEC was built to close
For many organisations, the challenge is no longer a lack of cybersecurity investment. It is maintaining visibility across increasingly fragmented digital environments.
“Malaysian enterprises aren't short of security tools; they're short of unified visibility,” Shanti says. “Chief executives should ask where visibility and ownership break down across cloud platforms, hybrid infrastructure and third-party ecosystems. Those gaps are often where incidents begin.”
This challenge also shaped TM CYDEC, TM's Cyber Fusion operating model for enterprise, government and critical infrastructure customers. Rather than treating network, cloud and cyber risks separately, the model brings visibility, threat intelligence and response capabilities into a more integrated operating environment.
For Shanti, the principle is straightforward: attackers do not operate according to an organisation's internal structure.
“A threat can move across your network, cloud environment, applications and third-party connections without caring which team owns what,” she says. “The organisation needs enough visibility across those boundaries to understand what is happening and act quickly.”
Looking ahead, TM One plans to progressively enhance TM CYDEC through AI Assurance, a set of capabilities designed to identify weaknesses in AI systems, protect them while they are in use, and help organisations adopt AI with greater confidence.
As organisations accelerate AI adoption and deliver more services digitally, trust is becoming a strategic asset that boards can no longer take for granted. According to Shanti, the question is no longer whether organisations can innovate, but whether customers, regulators and stakeholders trust them to do so responsibly.
For Shanti, digital trust is ultimately practical. Organisations need clear accountability, visibility over their digital environment and confidence that capable people can act when an incident occurs. Technology and governance have to work together if customers and stakeholders are to trust increasingly digital and AI-enabled services.
TM is also strengthening its own AI governance. It recently became the first Malaysian telco to earn the ISO/IEC 42001:2023 AI Management System certification, independently validated by SIRIM QAS International.
Sharing next steps, Shanti suggests organisations test their readiness against four questions:
> Who is accountable for AI decisions?
> Can management see risks across the organisation’s digital environment?
> Can management respond quickly during an incident?
> Can critical services continue while the incident is being handled?
Governance and monitoring should develop alongside AI adoption, not after a breach forces the issue.
“The next generation of market leaders will not be defined by how quickly they adopt AI,” she says.
“They will be judged by whether customers, regulators and stakeholders trust them to use it responsibly. That makes trust a leadership responsibility.”
Thank you for your report!
Empowering generations through responsible investment
Hamilton Biodiversity Park: Restoring life to a fragmented landscape
When life takes an unexpected detour
TM网络防御中心(CYDEC)是TM One的下一代安全运营中心。
马来西亚各组织正在迅速行动,将人工智能(AI)应用于实际工作中。
董事会都在追踪应用案例、生产力提升和节省时间。但有一个问题却很少受到关注:当人工智能系统泄露敏感信息、做出错误决策或被攻击者操纵时,谁该承担责任?
对于 TM One 执行副总裁 Shanti Jusnita Johari 而言,弥合问责差距必须成为领导层的首要任务。
随着人工智能逐渐融入运营、客户互动和决策制定等各个环节,问责制正成为当今董事会面临的关键治理挑战之一。
“董事会不应只关注人工智能部署的速度,还应该关注一旦出现问题,组织是否还能履行对客户和公民的承诺,”她说道。“这关乎领导力。”
董事会的一项授权
网络安全已从IT部门的一项常规任务转变为董事会必须关注的重点。董事会必须像对待财务、运营和监管风险一样,严格管控网络和人工智能风险。随着人工智能、云计算和自动化成为企业运营的核心,任何一起安全事件都可能扰乱运营、削弱信任、中断供应链,并引发监管方面的后果。
因此,领导者需要明确责任,界定组织对网络风险的容忍度,并确保业务连续性计划得到测试,而不仅仅是记录在案。
“网络安全不是成本中心,而是企业安心开展业务的必要条件,”Shanti解释道。“董事会应该要求提供证据,证明关键服务在发生安全事件时能够继续运行,而不仅仅是要求企业保证安全工具已到位。”
随着这些风险的出现,马来西亚的监管环境也在不断发展。《2024年网络安全法》规定了国家关键信息基础设施运营商的法定义务,包括风险评估、审计和事件通报;而国家网络安全局的《2025-2030年马来西亚网络安全战略》则制定了该国未来五年的网络安全韧性发展路线图。
人工智能的快速普及更凸显了其紧迫性。短短两年内,国家人工智能办公室发展成为马来西亚人工智能局(AI Malaysia),一个负责指导“2030年人工智能国家”愿景的中央级机构,其中包括马来西亚人工智能安全研究所,该研究所负责模型测试和红队演练。与此同时,根据AIBP发布的《2025/2026年人工智能准备度调查》,企业人工智能的采用率自2020年以来几乎翻了一番。
“这些转变反映了马来西亚将网络韧性视为国家要务的举措,”Shanti表示。“对董事会而言,这意味着从一开始就将韧性纳入人工智能议程,明确责任归属、投资方向,并在领导层审查进展情况。”
Shanti表示,马来西亚企业缺乏统一的可视性,这有助于识别风险并在风险演变成重大事件之前做出应对。
除了提升效率,人工智能也改变了攻防双方的数字化博弈格局。攻击者可以自动进行侦察、生成钓鱼内容,并比以往更快地调整策略。与此同时,各组织机构也在加速将人工智能应用于运营、客户互动和决策制定等各个环节。
对领导者而言,挑战不再仅仅是部署人工智能。治理、透明度和问责制也必须以同样的速度发展。
对Shanti而言,人工智能最大的影响之一在于缩短了决策时间。威胁能够被更快地识别、调整和应对,同时组织内部的互联互通程度和自动化程度也越来越高。因此,洞察局势并迅速采取行动的能力,其重要性与安全技术本身不相上下。
近期行业研究表明,网络安全事件的成本和复杂性都在不断增加。IBM发布的《2026年数据泄露成本报告》指出,全球平均数据泄露成本已达创纪录的499万美元,较上年增长12%,其中四分之一的恶意泄露事件是由人工智能驱动的攻击造成的。
就马来西亚国内而言,Pikom发布的《超越合规:2026年马来西亚网络安全韧性状况》报告指出,马来西亚数据泄露的平均成本在2025年攀升至320万令吉,高于前一年的290万令吉,一些机构报告称,单次事件造成的损失超过500万令吉。人工智能生成的网络钓鱼或深度伪造身份冒充如今已成为马来西亚机构面临的最常见攻击之一。
“对领导层来说,关键在于决策速度,”她说道。“组织能否及早发现威胁,了解其影响,并在事态升级前做出正确的决策?购买更多工具并不能自动赋予你这种能力。”
TM CYDEC 提供集成的端到端网络安全服务,包括 24/7/365 网络威胁监控和主动防御。
CYDEC™ 的建立旨在弥合这一差距。
对许多组织而言,挑战不再是网络安全投入不足,而是如何在日益碎片化的数字环境中保持可见性。
“马来西亚企业并不缺乏安全工具;他们缺乏的是统一的可见性,”Shanti说道。“首席执行官们应该探究在云平台、混合基础设施和第三方生态系统中,可见性和所有权在哪些方面存在脱节。这些漏洞往往是安全事件的源头。”
这一挑战也促成了TM CYDEC的诞生,这是TM面向企业、政府和关键基础设施客户的网络融合运营模式。该模式并非将网络、云和网络风险割裂处理,而是将可视性、威胁情报和响应能力整合到一个更加一体化的运营环境中。
对 Shanti 来说,这个原则很简单:攻击者不会按照组织的内部结构行事。
她表示:“威胁可以跨越您的网络、云环境、应用程序和第三方连接进行传播,而无需考虑哪个团队负责哪个方面。组织需要具备足够的跨边界可见性,才能了解正在发生的事情并迅速采取行动。”
展望未来,TM One 计划通过 AI Assurance 逐步增强 TM CYDEC,AI Assurance 是一套旨在识别 AI 系统中的弱点、在使用过程中保护它们以及帮助组织更有信心地采用 AI 的功能集。
随着企业加速采用人工智能并以数字化方式提供更多服务,信任正成为董事会不可再视为理所当然的战略资产。Shanti认为,问题不再是企业能否创新,而是客户、监管机构和利益相关者是否信任企业能够负责任地进行创新。
对Shanti而言,数字信任最终取决于实际操作。组织需要明确的问责机制、对其数字环境的可视性,以及对事件发生时能够由有能力的人员采取行动的信心。如果客户和利益相关者想要信任日益数字化和人工智能化的服务,技术和治理必须协同运作。
TM也在加强自身的AI管理。该公司最近成为马来西亚首家获得ISO/IEC 42001:2023人工智能管理体系认证的电信公司,该认证由SIRIM QAS International独立验证。
Shanti在分享后续步骤时建议各组织根据以下四个问题来检验自身的准备情况:
谁该为人工智能的决策负责?
管理层能否看到组织数字化环境中存在的风险?
管理层能否在事件发生时迅速做出反应?
在处理事件期间,关键服务能否继续运行?
治理和监控应该与人工智能的普及同步发展,而不是在发生安全漏洞之后才被迫重视。
“下一代市场领导者将不再以他们采用人工智能的速度来定义,”她说道。
“评判他们的标准在于客户、监管机构和利益相关者是否信任他们能够负责任地使用这项技术。因此,信任是领导者的责任。”
感谢您的报告!
通过负责任的投资赋能子孙后代
汉密尔顿生物多样性公园:恢复破碎景观的生命力
当生活发生意想不到的转折