Hundreds of federal websites lack key defense against spies, senator says参议员称,数百个联邦网站缺乏抵御间谍活动的关键防御措施。
The list includes sites for FBI tips, intelligence job applications, and the Veterans Crisis Line.
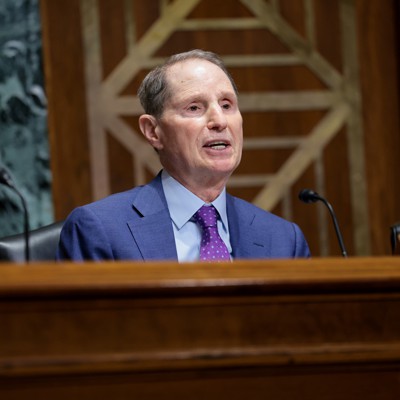
Sen. Ron Wyden, D-Oregon, speaks during a hearing on April 15, 2026, in Washington, D.C. Anna Moneymaker/Getty Images
The list includes sites for FBI tips, intelligence job applications, and the Veterans Crisis Line.
Sen. Ron Wyden, D-Ore., is urging the Trump administration to close an encryption gap that could let foreign adversaries track visits to sensitive government websites, including the FBI’s tip portal and a veterans crisis line, according to a letter sent to the Cybersecurity and Infrastructure Security Agency and the Office of Management and Budget on Monday and first seen by Nextgov/FCW .
Wyden asked CISA and OMB to require that agencies implement a web security standard that hides the name of the website someone is visiting. The protocol, known as Encrypted Client Hello, protects the website name when a user’s browser connects to a site and has been supported by major browsers and some web infrastructure providers since 2023.
Wyden’s office identified 350 federal web addresses that lack the encryption specification. They include sites that facilitate intelligence community job applications, immigration services, health information, and U.S. diplomatic websites around the world.
“This visibility could lead to malicious eavesdroppers identifying whistleblowers, profiling cleared federal personnel, tracking Americans seeking crisis support, and mapping interactions between agencies,” Wyden wrote to CISA acting director Nick Andersen and deputy federal chief information officer Thomas Flagg.
He also asked OMB, working with CISA and the Office of the National Cyber Director, to require that cloud and network providers support the technology to qualify for federal contracts. He requested responses by Nov. 20.
Nextgov/FCW has requested comments from CISA and OMB.
Federal websites generally encrypt the information people read or submit, though hackers can still learn which sites they visit by monitoring their internet traffic.
The letter singles out two services whose visitors could be particularly vulnerable.
The Department of Veterans Affairs’ Veterans Crisis Line platform uses Amazon Web Services, which does not currently support ECH for the site, according to the letter. Wyden warned that the exposure could help foreign adversaries identify veterans seeking mental health assistance. Additionally, the FBI’s tips.fbi.gov site uses Cloudflare, a provider that supports ECH, but the portal has not enabled it, the senator added, arguing the current arrangement could put people contacting the bureau at risk of identification.
The possible FBI exposure also comes after a prolific criminal hacker group recently stole troves of sensitive employee information tied to the bureau’s jobs portal.
The list of sites without the protocol also includes hotline.oig.dhs.gov, the DHS inspector general’s complaint hotline; civilrights.justice.gov, the Justice Department’s civil rights reporting portal; and apply.intelligencecareers.gov, an intelligence community recruitment site. Federal HIV information sites, including hivinfo.nih.gov and clinicalinfo.hiv.gov, are also listed.
To craft the list, Wyden’s staffers tested federal web addresses using third-party network providers to see if ECH successfully hid which specific websites were being visited, a spokesperson told Nextgov/FCW . The protection only appeared to work on sites relying on Cloudflare’s free service tier, the spokesperson added.
The letter does not establish that adversaries have tracked visitors to any of the listed addresses.
Wyden argued the government can close these gaps using technology already supported by major browsers and deployed across millions of websites. For agencies whose providers support ECH, enabling it can be as simple as changing a setting, he said.
“Modern federal zero trust cybersecurity practices rely on protective software installed directly on agency devices, so enabling [Encrypted Client Hello] would strictly improve the cybersecurity of federal networks,” Wyden wrote.
The effort follows his September call for NSA to update its advice about virtual private networks. A Congressional Research Service analysis requested by his office at the time warned that foreign intelligence services with broad visibility into internet traffic could potentially connect VPN users to websites by comparing traffic patterns.
NEXT STORY: Marines fielding new tech for prolonged medical care on the battlefield
2026年4月15日,俄勒冈州民主党参议员罗恩·怀登在华盛顿特区举行的听证会上发表讲话。(图片来源:Anna Moneymaker/Getty Images)
该列表包括 FBI 举报网站、情报工作申请网站和退伍军人危机热线网站。
据 Nextgov/FCW 周一收到的一封致网络安全和基础设施安全局以及管理和预算办公室的信函显示,俄勒冈州民主党参议员罗恩·怀登敦促特朗普政府填补一个加密漏洞,该漏洞可能让外国敌对势力追踪对敏感政府网站的访问,包括 FBI 的举报门户网站和退伍军人危机热线。
怀登要求网络安全和基础设施安全局 (CISA) 和管理和预算办公室 (OMB) 强制各机构实施一项网络安全标准,以隐藏用户正在访问的网站名称。这项名为“加密客户端 Hello”的协议可在用户浏览器连接到网站时保护网站名称,自 2023 年以来已得到主流浏览器和部分网络基础设施提供商的支持。
怀登的办公室发现了350个缺少加密规范的联邦政府网站地址。这些网站包括情报机构的求职申请网站、移民服务网站、健康信息网站以及美国在全球的外交网站。
“这种可见性可能导致恶意窃听者识别举报人、分析获得安全许可的联邦人员、追踪寻求危机援助的美国人以及绘制机构间的互动图,”怀登在写给CISA代理主任尼克·安德森和联邦副首席信息官托马斯·弗拉格的信中说道。
他还要求管理和预算办公室(OMB)与网络安全和基础设施安全局(CISA)以及国家网络安全总监办公室合作,要求云服务和网络提供商必须支持相关技术才能获得联邦合同。他要求在11月20日前收到回复。
Nextgov/FCW 已向 CISA 和 OMB 征求意见。
联邦政府网站通常会对用户阅读或提交的信息进行加密,但黑客仍然可以通过监控用户的网络流量来了解他们访问哪些网站。
信中特别指出了两项服务,这两项服务的访客可能特别容易受到伤害。
根据信函内容,美国退伍军人事务部“退伍军人危机热线”平台使用亚马逊网络服务(AWS),而AWS目前不支持该网站的电子通信技术(ECH)。怀登警告称,这种信息泄露可能有助于外国敌对势力识别寻求心理健康帮助的退伍军人。此外,怀登还补充道,联邦调查局的tips.fbi.gov网站使用Cloudflare,该服务提供商支持ECH,但该网站尚未启用此功能。他认为,目前的安排可能会使联系联邦调查局的人员面临身份泄露的风险。
此次FBI可能被曝光的情况,也发生在一个活跃的黑客犯罪团伙最近窃取了与该局招聘门户网站相关的大量敏感员工信息之后。
未遵守该协议的网站列表还包括:国土安全部监察长投诉热线 hotline.oig.dhs.gov;司法部民权举报门户网站 civilrights.justice.gov;以及情报界招聘网站 apply.intelligencecareers.gov。此外,联邦政府的艾滋病信息网站,例如 hivinfo.nih.gov 和 clinicalinfo.hiv.gov 也位列其中。
一位发言人告诉Nextgov/FCW,为了编制这份名单,怀登的幕僚使用第三方网络提供商测试了联邦政府的网址,以检验ECH是否能成功隐藏用户正在访问的具体网站。该发言人补充说,这种保护措施似乎只对使用Cloudflare免费服务的网站有效。
信中并未证实敌对势力已追踪到所列任何地址的访客。
怀登认为,政府可以利用主流浏览器已支持且已部署在数百万个网站上的技术来弥补这些差距。他表示,对于那些服务提供商支持电子通信技术的机构而言,启用这项技术只需更改一个设置即可。
怀登写道:“现代联邦零信任网络安全实践依赖于直接安装在机构设备上的保护软件,因此启用[加密客户端 Hello]将大大提高联邦网络的网络安全。”
此前,他曾在9月份呼吁美国国家安全局更新其关于虚拟专用网络(VPN)的建议。当时,他的办公室委托国会研究服务处进行的一项分析警告称,对互联网流量拥有广泛监控权限的外国情报机构,可能通过比较流量模式,将VPN用户与特定网站关联起来。
下一篇报道:海军陆战队部署新技术,用于战场上的长期医疗护理