How the Pentagon wants to buy cyber outcomes, not equipment五角大楼想要购买的是网络安全成果,而不是设备。
The Pentagon has been exploring a new paradigm dubbed Cyber Effects-as-a-Service, aiming to purchase specific outcomes as opposed to bespoke capabilities.
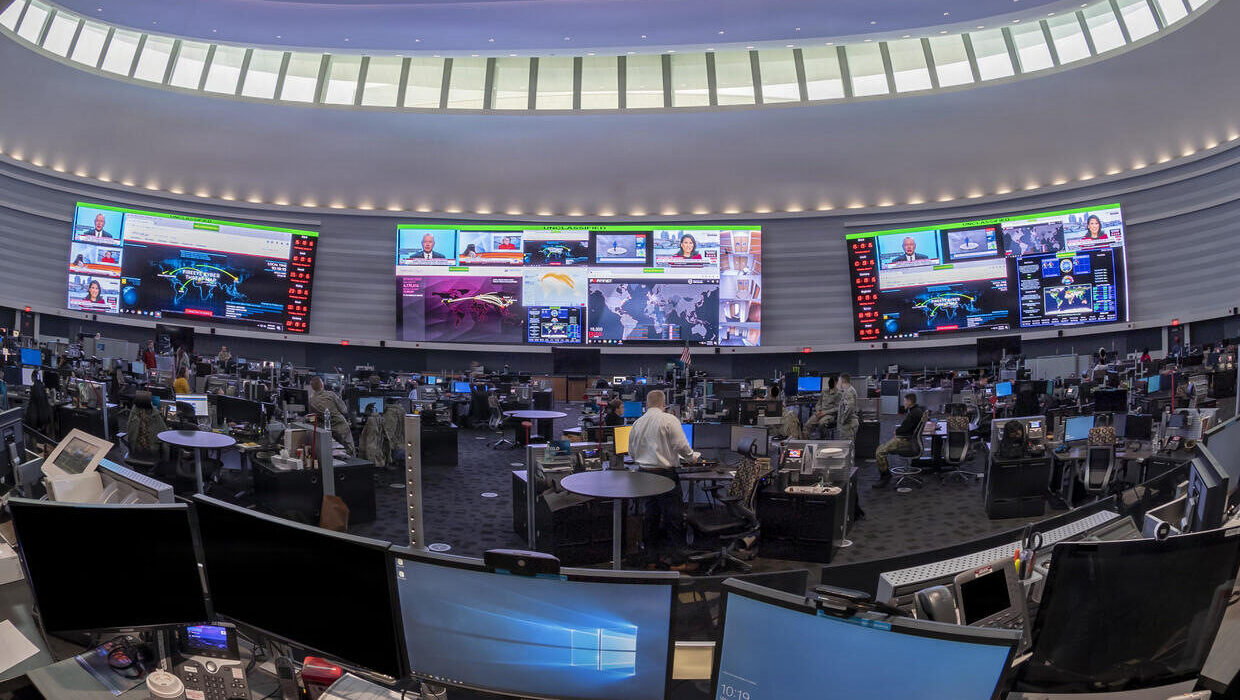
Personnel from both the NSA and U.S. Cyber Command work closely in the ICC to achieve national security objectives. (NSA)
WASHINGTON — To keep up with the demand of new technology and capabilities while threats in cyberspace quickly evolve, over the last several months the Pentagon has been pushing a new paradigm that calls for more direct contractor involvement in operations.
The idea is known as Cyber Effects-as-a-Service (CEaaS), a model that is focused on contracting for specific outcomes as opposed to specific tools.
“I’m focused on one single priority, and that is building a more robust set of capabilities for the [defense] secretary and the president. The demand signal that we see across all of our leadership in the department, our combatant commanders … far exceeds the supply we have,” Katie Sutton, assistant secretary of defense for cyber policy, said in September.
Sutton, in several remarks over the past month, has charged that the relationship between industry and the government must change. While this is a common refrain of officials across many administrations, in the unique landscape of cyberspace, Sutton has described a desired framework of moving from “contractual relationship to an operational partner” with industry and relying more on their know how in the technology space to push “concepts and ways of thinking about things that are out of the box [and] bringing new ideas way more quickly than we can.”
Politico first reported last month that drafts of the forthcoming Department of Defense cyber strategy show the Pentagon wants contractors to play a bigger role in conducting operations themselves.
To get an idea about why the change is coming now, how CEaaS would work, inherent risks involved and what the Pentagon wants from industry as it looks for a more operational partnership, Breaking Defense spoke to over a dozen sources spanning current industry, former Pentagon officials and members of academia.
They explained the push for more cooperation is coming both from the private sector and the government.
Bringing real autonomy to battlefield drone swarms
Decentralized Embodied Collaborative intelligence enables better reconnaissance, logistics and combat capabilities.
A former Pentagon official said there are companies in the start-up world looking to make this type of operational model their bread and butter, while some more traditional companies and primes are lobbying to be the leaders in this space. But, the government right now is looking to favor smaller, start-up type organizations funded through private equity and venture capital (VC), the former official added, especially since younger companies are cheaper for the government.
Sutton said in September that she’s really excited to see the shift over the last five years of particularly funding for companies that are focused on different cyber effects, particularly cyber effects operations. Seen a lot of interest in the VC community. Continuing to support that, continuing to find ways to bring them in.”
The Pentagon is approaching various commercial companies to see where this concept can take hold.
Sutton’s office hosted a tabletop exercise in late September with members of industry across the AI and defense technology sectors along with US Cyber Command. The event sought to game out how the Pentagon can build “new operational models with industry to deliver cyber outcomes at the speed, scale, and complexity required by the modern threat environment.”
The DoD’s release didn’t say exactly what was learned from the tabletop exercise, but offered the discussion moved from broad concepts to practical implementation. The Pentagon plans to use the findings of the event to refine the CEaaS framework and identify near-term opportunities.
Cyber Warfare Start-Ups
The current model for conducting cyber operations is too antiquated in the modern world and against modern threats, according to government officials and industry experts.
“The current paradigm for how cyber operations are conceptualized, resourced, and conducted, stemming from the signals intelligence realm, is incompatible with the requirements of modern military operations,” Joe Lin, co-founder and CEO at Twenty, a venture-capital-backed cyber warfare startup, said in an interview. “We need capabilities that provide the options needed for decision-makers and commanders to respond across the spectrum of competition and conflict.”
Under the traditional model, the government publishes requests for capabilities for industry to bid on and provide the expertise, manpower and tooling to provide exactly what the government asked for. Currently, it is very common for industry to also provide support in planning for operations and even sit side-by-side with operators.
However, the emerging CEaaS model aims to solicit specific outcomes as opposed to bespoke tools, under the direction and oversight of the government sources indicated.Essentially this means companies aren’t going out on their own and picking their own targets.
The Pentagon described CEaaS in its release highlighting the tabletop exercise as “a model for purchasing mission-ready cyber outcomes under Department direction and oversight. DoW retains responsibility for objectives, authorizations, and inherently governmental functions, while industry provides the technical expertise, tradecraft, and innovation needed to deliver authorized outcomes.”
Outcomes could be a requirement to gain access to a particular network, for example, in which the company performs that operation using its own people, tools and infrastructure or in concert with military operators.
Many of the officials and industry figures with whom Breaking Defense spoke with said it’s a little too early to tell what this will look like in practice, but acknowledged a potential scenario could be the government hiring a private firm to gain access to an adversary’s networks to perform a specific mission, like access or some type of disruption.
In the physical world, this would be akin to contractor-owned, contractor-operated intelligence, surveillance and reconnaissance flights in which companies use their own personnel and aircraft to watch targets in the air under the direction of the Pentagon. Where CEaaS would go a step further, is if the aircraft left friendly airspace to get a better view into hostile territory, leaving the hypothetical contractor-owned plane in enemy airspace as a direct combatant.
“We cannot rely on legacy processes alone to meet a machine-speed threat. We need outcomes-focused relationships that pair government direction and accountability with the unmatched innovation of the American private sector,” Sutton said in the Pentagon’s release.
The Trump administration has sought to gain more support from the private sector in cyberspace. In August, it issued an executive order outlining a framework for private companies to conduct operations against transnational criminal organizations under the Department of Justice and Homeland Security, a framework that is still being developed.
Similarly, the Senate-passed annual policy bill included a provision authorizing a pilot program for the Pentagon to enlist contractors to perform access operations on their own infrastructure .
But similar to the transnational criminal framework, experts who spoke to Breaking Defense have questions as to how a CEaaS would work in practice, and outlined the risks associated with private sector actors performing these operations, even if under the guidance of the government.
While details are still nascent on exactly how this model will work in practice, sources acknowledged the department sees a larger role for industry participation.
“The hard part is, what is the end-to-end operational model going to look like, especially because if the government is going to own the control of the operation — as they should — I don’t think industry can come in and say we can guarantee the outcome,” a senior cyber official at a defense firm told Breaking Defense. “It gets difficult to guarantee an outcome when it comes to cyberspace operations.”
A second former Pentagon official noted that the outcome-based model is attractive because industry’s commercial tools are ready to go to immediately solve problems rather than the more amorphous model of asking a company to build a capability that military operators will then have to integrate into operations themselves.
But, the industry official added that the government still needs to figure out what exactly it wants industry to do from an operational standpoint, be it going after non-state groups such as criminal actors or taking on higher risk efforts against nation states.
For instance, Gary Corn, former Staff Judge Advocate at CYBERCOM and current director of the Technology, Law and Security program at American University, outlined the risk companies and their operators could be assuming .
“If companies start engaging in out-of-network effects operations off of their own networks and infrastructure, that might trigger adversaries to respond,” Corn said. “Those companies are now potentially more relevant or advantageous targets for the enemy. Those companies and individuals are potentially exposed to criminal and civil liabilities outside of the United States, where immunities or defenses that might be available under domestic law would not exist to protect them.”
The one area the second former official said the Pentagon should take caution with is how these contracts or opportunities are communicated or worded. A request for an outcome that is too specific could alert adversaries of a gap in Pentagon capabilities. If the requests go beyond broadly outlining the desire for effects against certain things and gets overly specific, it can demonstrate gaps in government capabilities because it shows the military might not have the ability to do that right now.
For Jason Healey, senior research scholar at Columbia University, he is more concerned about the governance of such a program.
“If poorly governed and successful, the Pentagon will decide that if a little dependence on contractors is good, then a lot must be way better. The program will get out of hand with contractors conducting far more operations than is wise against the intelligence and military forces of nuclear-armed rivals,” he said. “If poorly governed and unsuccessful, the Pentagon may decide that they need to further remove restraints, engaging yet more persistently and taking even greater risks.”
While allowing contractors more autonomy to conduct cyber operations themselves — something that has typically been reserved for the government — is a departure from norms, some experts who spoke to Breaking Defense believe this is a natural evolution of the cyber landscape.
“As much as we’ve invested resources into the government cyber enterprise, we just don’t have enough capacity to address all the threats,” Corn said in an interview. “The front lines of this conflict space are shifting to the private sector. The pressure has been building, steadily over time to move public-private collaboration beyond just what have been anemic discussions and frameworks around information sharing.”
Harnessing the private sector in a bigger way makes a lot of sense to many, given that tech companies, not the government, build cyberspace and are at the cutting edge of emerging technologies.
“Industry has a lot of capability that can be taken more advantage of,” Robert Skinner, former commander of Cyber Defense Command, said in an interview.
“On a cyber effects standpoint, there’s a lot of capability out there. Because oh, by the way, a lot of those companies are developing the tools that the government uses already. So why not be able to take full advantage of the force that they have?” Skinner, who currently serves as chairman of the board for Axonius Federal Systems, added.
Breaking Defense Video
The new must-have capabilities for drones [Sponsored]
Army’s tech chief talks autonomy, acquisition and the future of drones
Drones take over AUSA, plus the Army’s plan to bring in new vendors
Hegseth talks autonomy at AUSA, a key show focus
Army doubles down on autonomy, stakes out Indo-Pacific role: AUSA Day 2
Telle talks ‘manufacturing rodeo,’ supply chain ‘weak links’: AUSA Day 1
New leaders, new drone command: What we expect from AUSA 2026
Unpacking Boeing’s F/A-XX win, plus a report from wartime Ukraine
How Hegseth envisions a new Autonomous Warfare Command
What Europe’s military air fleets will look like in 30 years
美国国家安全局和美国网络司令部的人员在信息通信技术中心密切合作,以实现国家安全目标。(美国国家安全局)
华盛顿——为了跟上新技术和新能力的需求,同时应对网络空间威胁的快速演变,在过去的几个月里,五角大楼一直在推动一种新的模式,即要求承包商更直接地参与行动。
这种理念被称为网络效应即服务 (CEaaS),该模式侧重于签订特定结果的合同,而不是签订特定工具的合同。
“我目前只专注于一个优先事项,那就是为国防部长和总统构建一套更强大的能力体系。我们从国防部所有领导层、作战司令部……都看到了远远超过我们现有能力的呼声,”负责网络政策的国防部助理部长凯蒂·萨顿在9月份表示。
在过去一个月里,萨顿多次发表讲话,指出产业界与政府之间的关系必须改变。虽然这在许多届政府的官员中都是老生常谈,但在网络空间这一独特的领域,萨顿描述了一种理想的框架,即从与产业界的“合同关系”转变为“运营伙伴”,更多地依靠他们在技术领域的专业知识来推动“跳出固有思维模式的概念和思考方式,并比我们更快地提出新想法”。
Politico 上个月率先报道称,即将出台的国防部网络战略草案显示,五角大楼希望承包商在开展行动方面发挥更大的作用。
为了解为何现在会发生这种变化、CEaaS 将如何运作、其中存在的固有风险以及五角大楼在寻求更具运营性的合作伙伴关系时希望从业界获得什么,《防务新闻》采访了十几位消息人士,其中包括当前业界人士、前五角大楼官员和学术界人士。
他们解释说,推动加强合作的呼声来自私营部门和政府两方面。
赋予战场无人机群真正的自主性
去中心化具身协作智能能够提升侦察、后勤和作战能力。
一位前五角大楼官员表示,一些初创企业正试图将这种运营模式作为其主要盈利模式,而一些较为传统的公司和大型企业则在游说,希望成为该领域的领导者。但这位前官员补充说,目前政府更倾向于扶持规模较小、由私募股权和风险投资(VC)资助的初创企业,尤其因为对于政府而言,年轻的公司成本更低。
萨顿在九月份表示,她非常高兴地看到过去五年来,专注于不同网络效应(尤其是网络效应行动)的公司获得了更多资金。她注意到风险投资界对此表现出浓厚的兴趣。她将继续支持这些公司,并继续寻找吸引他们参与的方法。
五角大楼正在与多家商业公司接洽,探讨这一理念在哪些领域能够落地生根。
萨顿的办公室在9月下旬组织了一次桌面演练,人工智能和国防技术领域的业界人士以及美国网络司令部都参与了此次演练。演练旨在探讨五角大楼如何与业界合作,构建“新的作战模式,以在现代威胁环境所需的速度、规模和复杂性下交付网络安全成果”。
美国国防部发布的新闻稿并未具体说明桌面演练的具体成果,但表示讨论已从宏观概念转向实际应用。五角大楼计划利用此次演练的成果完善CEaaS框架,并确定近期可实现的机遇。
网络战初创公司
政府官员和行业专家表示,当前网络作战模式在现代世界和面对现代威胁时过于陈旧。
“目前网络作战的概念化、资源配置和实施方式都源于信号情报领域,这与现代军事行动的需求并不相符,”风险投资支持的网络战初创公司Twenty的联合创始人兼首席执行官Joe Lin在一次采访中表示。“我们需要能够为决策者和指挥官提供应对各种竞争和冲突所需选项的能力。”
在传统模式下,政府发布能力需求征集书,企业可以参与竞标,并提供所需的技术、人力和工具,以满足政府的特定需求。目前,企业参与运营规划,甚至与运营人员并肩工作,也十分普遍。
然而,新兴的CEaaS模式旨在寻求特定成果,而非定制工具,并在上述政府机构的指导和监督下进行。这实质上意味着企业不能自行其是,也不能自行选择目标。
五角大楼在新闻稿中将CEaaS描述为“在国防部的指导和监督下,采购可立即执行任务的网络成果的模式。国防部负责目标、授权和固有的政府职能,而业界则提供交付授权成果所需的技术专长、专业技能和创新。”
例如,结果可能是获得特定网络访问权限的必要条件,在这种情况下,公司可以使用自己的人员、工具和基础设施或与军事人员合作来执行该操作。
Breaking Defense 采访的许多官员和业内人士表示,现在判断这在实践中会是什么样子还为时过早,但他们承认,一种可能的情况是,政府雇佣一家私营公司来获取敌方网络的访问权限,以执行特定任务,例如访问或某种类型的破坏。
在现实世界中,这类似于承包商拥有并运营的情报、监视和侦察飞行,即公司使用自己的人员和飞机,在五角大楼的指挥下监视空中目标。而CEaaS更进一步,如果飞机离开友方空域以更好地观察敌方领空,那么这架假想的承包商拥有的飞机就进入了敌方空域,成为直接的作战力量。
“我们不能仅仅依靠传统流程来应对机器速度带来的威胁。我们需要以结果为导向的合作关系,将政府的指导和问责与美国私营部门无与伦比的创新能力结合起来,”萨顿在五角大楼发布的新闻稿中说道。
特朗普政府一直寻求在网络空间获得私营部门的更多支持。今年8月,它发布了一项行政命令,概述了私营公司在司法部和国土安全部领导下开展打击跨国犯罪组织的行动框架,但该框架仍在完善中。
同样,参议院通过的年度政策法案中包含一项条款,授权五角大楼开展试点项目,招募承包商对其自身的基础设施进行接入操作。
但与跨国犯罪框架类似,接受 Breaking Defense 采访的专家们对 CEaaS 在实践中如何运作提出了疑问,并概述了私营部门参与者执行这些行动(即使是在政府的指导下)所带来的风险。
虽然该模式在实践中将如何运作的具体细节尚不明确,但消息人士承认,该部门认为行业参与将发挥更大的作用。
一位国防公司的高级网络安全官员告诉《防务新闻》:“难点在于,端到端的作战模式究竟会是什么样子,尤其是在政府要掌控作战指挥权的情况下——他们理应如此——我认为业界无法介入并声称我们能够保证结果。”他补充道:“在网络空间作战中,结果很难保证。”
另一位前五角大楼官员指出,基于结果的模式很有吸引力,因为行业内的商业工具已经准备就绪,可以立即解决问题,而不是像要求公司构建某种能力,然后由军事操作人员自行将其整合到作战行动中那样,这种模式更加模糊不清。
但这位业内人士补充说,政府仍然需要从操作层面弄清楚它究竟想让业界做什么,无论是打击犯罪分子等非国家行为体,还是承担针对民族国家的高风险行动。
例如,美国网络司令部前参谋法官、现任美国大学技术、法律和安全项目主任加里·科恩概述了公司及其运营者可能面临的风险。
科恩表示:“如果企业开始在自身网络和基础设施之外进行网络外效应操作,这可能会引发对手的报复。这些企业现在可能成为敌方更具相关性或更有利的目标。这些企业和个人可能面临美国境外的刑事和民事责任,因为在境外,他们无法获得国内法律可能提供的豁免或辩护。”
第二位前官员指出,五角大楼应该谨慎对待的一个方面是这些合同或合作机会的沟通和措辞。对结果的要求过于具体,可能会让对手察觉到五角大楼能力上的不足。如果要求不只是笼统地概述对某些目标的预期效果,而是过于具体,就会暴露政府能力的缺陷,因为它表明军方目前可能不具备相应的能力。
哥伦比亚大学高级研究员杰森·希利更关心的是此类项目的管理。
“如果管理不善却取得成功,五角大楼就会认为,如果对承包商的少量依赖是好事,那么大量依赖肯定更好。这样一来,承包商就会对拥有核武器的对手的情报和军事力量进行远超明智范围的行动,导致项目失控,”他说道。“如果管理不善且失败,五角大楼可能会认为需要进一步放松限制,更加持续地参与其中,承担更大的风险。”
虽然允许承包商拥有更大的自主权来开展网络行动(这通常是政府的特权)与惯例有所不同,但一些接受 Breaking Defense 采访的专家认为,这是网络空间发展的自然趋势。
科恩在一次采访中表示:“尽管我们在政府网络安全领域投入了大量资源,但我们仍然没有足够的能力应对所有威胁。这场冲突的前线正在向私营部门转移。随着时间的推移,要求公私合作超越目前围绕信息共享的乏力讨论和框架的压力与日俱增。”
鉴于科技公司而非政府构建了网络空间,并且处于新兴技术的前沿,因此,更多地利用私营部门对许多人来说很有意义。
“业界拥有很多可以更好地利用的能力,”网络防御司令部前司令罗伯特·斯金纳在一次采访中表示。
“从网络效应的角度来看,目前已经有很多相关能力。因为,顺便一提,很多公司正在开发政府已经在使用的工具。那么,为什么不充分利用他们所拥有的力量呢?”现任Axonius Federal Systems公司董事长的斯金纳补充道。
突破性防御视频
无人机必备的新功能 [赞助内容]
陆军技术主管谈无人机的自主性、采购和未来
无人机主导了美国陆军协会(AUSA)的会议,此外,陆军还计划引入新的供应商。
Hegseth 在 AUSA 大会上谈到了自主性,这是本次大会的一个重点议题。
陆军加倍强调自主性,明确印太地区角色:AUSA第二天
特勒谈“制造业乱象”、供应链“薄弱环节”:AUSA 第一天
新领导人,新无人机指挥部:我们对 AUSA 2026 的期待
深入剖析波音F/A-XX的中标,以及来自战时乌克兰的报道
赫格塞斯设想的新型自主作战指挥部
30年后欧洲军用空军机队会是什么样子